
The UEFI 9/11 - Part VII - This Coming Week Many PCs Will Refuse to Boot "Linux" (Because of Microsoft's Expired Certificate)
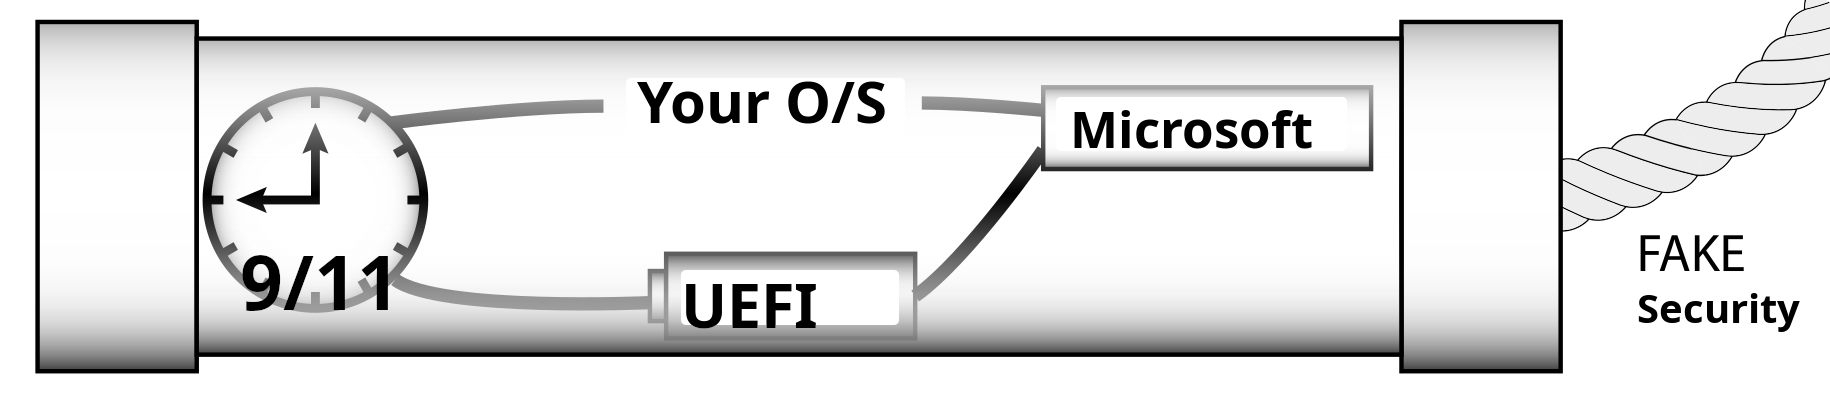
Love it or hate it, more and more people are moving to GNU/Linux and many PCs ship with UEFI. Many existing PCs already have it and have had it for years. Many are configured, by default, to use "secure boot". Many won't be able to cope with certificate rotation (the proprietary firmware blobs are notoriously buggy) and even if updates become available - which is far from a certainty - installing them is super-risky (in part because those are barely tested and are notoriously buggy; a lot can go wrong and if it goes wrong, undoing the harm is almost infeasible for an ordinary person; it's worse than Windows breaking things because this is done closer to the hardware - rendering this a chicken-and-egg problem a la locking oneself out).
This is why throughout the week we'll keep reminding people (here and in the sister site) to turn off "secure boot" or "SecureBoot". It's imperative for people who value reliability and resiliency, uptime, data security etc. Being locked out of one's own machine is a really bad outcome. We saw how it played out before, e.g. in 2020 [1, 2]. This is not security, this is just sheer madness.
Updating firmware is not a good option at this time (or any time). Quoting thelayoff.com on IBM (from yesterday): "Yes, your Lenovo laptop is spying on you and sending your information to China. After all, when you install BIOS updates, who knows what those BIOS updates really do. Do you ? Same as your "Made In China" cell phone and the wireless access points updates. Big Brother is China, not Trump. LOL."
It is not security when some opaque, proprietary blob from China gets put inside your system at a very low level, with access to pretty much everything including external peripherals like backup drives. Having a program running as "root" and allowing remote modifications of firmware is not security either. It's insanity! It is promoted by the same people who advocate Microsoft-controlled 'secure boot'.
Today we'd like to debate some more details and refrain from getting too technical; on Monday and Wednesday we'll be concluding ahead of the actual "9/11" of this monstrosity. When we say "9/11" we refer to Chile's 9/11 moment [1, 2]. We explained several analogies/parallels/parables in prior parts. We won't get political about this. It is about commercial ambitions, not political ideology.
In Part I we introduced the issues in simple terms, in Part II we focused on the attacks on people who merely talked about these issues, Part III primarily tied things together, Part IV named some of the culprits, and Part V advised people to turn off "SecureBoot" (also in the sister site now that we're in September; live and learn). Part VI spoke of the "Serious Harm" that will be caused to many ordinary computer users; many will not even understand what the heck is going on; they're too busy to keep abreast of "Linux news" online and they don't have an LWN subscription. Most of them lack a backup option such as a second PC and never in their lifetime saw a boot menu (they might not know that such a thing exists or how to enter/activate it). Heck, some OEMs already make PCS would not let the users disable "secure boot" or "SecureBoot"; some of them refuse to boot anything but Windows (we're looking at you, Lenovo). The issues are very serious - to the point where those responsible for the monopolistic abuse started attacking my wife [1, 2] and when attacking my wife wasn't enough they joined forces with a dangerously violent Serial Strangler from Microsoft. This is what I get for merely talking about those things.
So we should be talking more about those things.
What is it that's happening to the system? Well, UEFI will be checking the time on the system (there's a system clock) and the firmware can then decide whether to boot or not (or what to boot). Although there are few super-geeks out there who take it a step further (e.g. installing one's own keys), way more than 99% of PCs out there don't have the skills nor the setup. The users don't know how to modify these things. Almost nobody would do that also because it is risky (cannot change the firmware, that's for sure). Consider what happened in Red Hat. Even Red Hat with all its Linux engineers couldn't get this right. It's very risky (you can brick or break your system, so either you get kicked out by UEFI or you break your own system while trying to mitigate).
Don't tell people to open their PCs and remove the clock's battery; it would not work and almost nobody would open a laptop (the modern ones require special screwdrivers).
It is a basically a giant risk. Very much so. Don't try. And you should not have this risk to begin with; this not security but a lie. It was always a lie.
The real solution is, disable "secure boot" or "SecureBoot" while it's still possible. Microsoft and OEMs will try to make it infeasible, at risk of angering people (expected PR toll).
Just like submarine patents, a lot of this problem was "hibernating" for a while, in effect artificially contrived right from the beginning in 2011. And it's not a matter of whether it's coming; it's a question of when.
In collusion with Red Hat and Canonical and enabled by terrible people with their online mob ('cancel brigade'), Microsoft promoted this 'inevitable' outcome. This collusion got the courts off of Microsoft's back with no further investigation after that (saying that shim was somehow a solution). We can still recall a complaint started in Spain but not limited to Spain; the European Commission or European authorities were meant to look into it, but then the Microsofters stepped in, plus they were libelling everyone who did not agree with them. Matthew J. Garrett did this nonstop. He cannot even keep his Web site online (why trust him with your PC?).
Now he openly admits that someone pays him to attack me. He might end up causing serious harm to his sponsors. Judges are beginning to realise both cases - his and the Serial Strangler's - are conjoined and classic abuse of process done from another continent for a large company to gain. Are Free software community folks and Techrights readers up to the task of finishing this job and getting costs ordered against them and maybe the two Directors of the LLP, who facilitated and coordinated this abuse? It's hardly infeasible, based on my research as LIP. This matter will be covered separately some other day. █