
James Bottomley Has Promoted Microsoft-Controlled Restricted ('Secure') Boot, His Blog Has Just Been Cracked
Does this meet IBM's and Microsoft's standards for "distinguished" (in security)?
Earlier today James Bottomley's "random Pages" included casino and spam pages. His blog clearly got cracked. As proof of this (he has since then cleaned up or covered up):
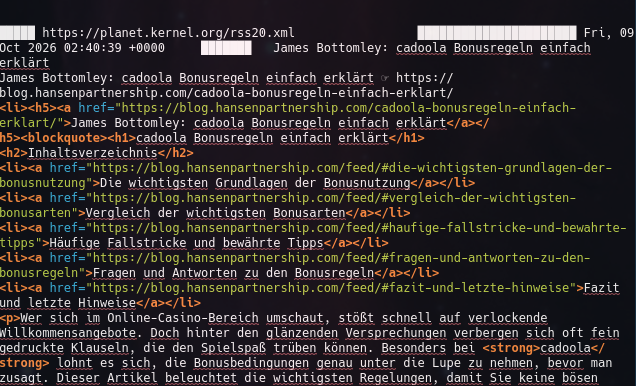
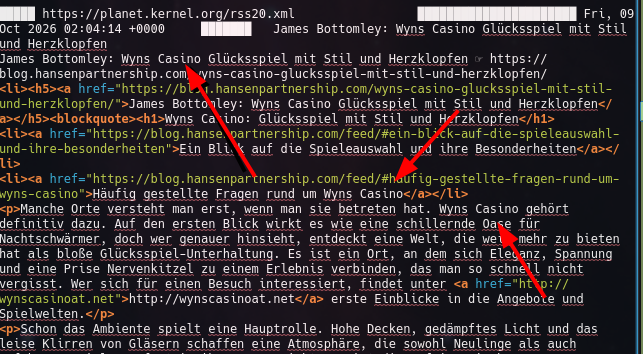

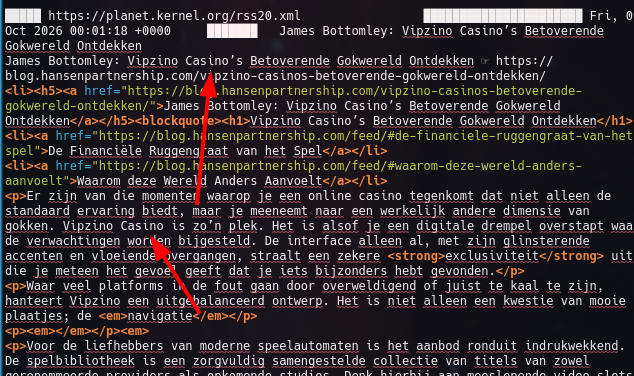
And at least six more like that.
Remember when he worked for Novell?
It's funny when people who lecture us on TPMs and 'secure' boot cannot get the basics right.
At least they can undo the knot of a bow tie. █
On security 'gurus' that promote Microsoft and vendor lock-in/kill switches: It Took a Long Time to Show What Jason Arday (at Cambridge) and Harvey Weinstein (in Hollywood) Really Were | Always Independently Verify What People Claim to Be (or Find Yourself in a Jason Arday-Type Moment/Dilemma)