
Bonum Certa Men Certa

DNS Suspended by Microsoft Windows Botnets

Warpath of Web destruction

TWO DAYS ago I was unable to use the Internet properly. This network's DNS servers came under massive attack at a time when hundreds of millions of Windows zombies ran rampant. It's neither a new problem [1, 2] nor does affect just the network that I'm on. There are similar complaints and status reports out there on the Web right now.

Potential Latency on Network Solutions DNS


There is a spike in DNS query volumes that is causing latency for the delay in web sites resolving. This is a result of a DDOS attack. We are taking measures to mitigate the attack and speed up queries

—————-

There may be some latency on Network Solutions DNS Severs and some queries may be timing out. This may include instances when someone types a domain name into a browser and the website will temporarily not resolve. Network Solutions Operations is working on optimizing the DNS queries and investigating the issue.


There is nothing that prevents a determined cracker (or a gang of them) from taking down DNS globally [18, 19], especially given Windows botnets of biblical proportions . This almost happened 2 years ago and there are still no effective defenses in place. The same goes for the scale of botnets -- a solution to which Microsoft cannot deliver.

"Microsoft slammed over security advice


US COMPUTER Emergency Readiness Team (US-CERT) has warned that Microsoft's advice about how to beat the Downadup worm is flawed.


And things are getting worse before they get better.

A security expert has managed to transfer the digital signature of one Windows program to another, without invalidating the signature. Didier Stevens, who presented the attack in his blog, exploited the fact that Microsoft's Authenticode code signing standard accepts the vulnerable MD5 hash algorithm. Stevens used this to generate two programs which have identical code signatures, but behave differently.
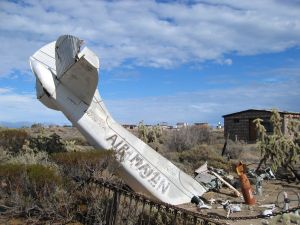

How long can this chaos [1, 2, 3] go on for? Many related news (2006-2008, re: DNS) are added as references below. ⬆

Airplane crash
What if aircrafts accepted Microsoft quality control?


_____ [1] Open source DNS server takes on BIND

Four companies led by Dutch non-profit NLnet Labs have launched an open source, Linux-compatible DNS (Domain Name System) server. "Unbound," which is also sponsored by VeriSign, Nominet, and Kirei, claims to offer a validating, recursive, and caching DNS server that is faster than the open source DNS mainstay BIND.


[2] VeriSign Takes Aim at Open Source DNS

Now VeriSign, the company that runs that .com and .net domains, is aiming to provide an open source alternative to BIND, called Unbound.


[3] SocialDNS: Free Domains for a Free Internet

John Sullivan (FSF) invited me to present in this mailing list the SocialDNS project (http://www.socialdns.net). I am very interested in obtaining feedback from the GNU community because we want to submit our project to the Free Software Directory soon.


[4] DNS Patches Slow Servers, but Fast Action Is Advised

Microsoft issued a mea culpa about its DNS update on July 17, saying that the patch was crippling some machines running its Windows Small Business Server suite. Then, on July 25, it said the patch could also affect some network services on systems running Windows Server 2008, Windows Server 2003 and Windows 2000. In both instances, Microsoft detailed work-arounds.


[5] DNS poisoners hijack typo domains

People arrive at these pages when the domain name they request is unavailable, because, for example, they mistyped the URL. ISPs use this redirection method, known as Typosquatting, to advertise free domains or competing products. In the present case, however, clients don't arrive on the Typosquatter pages, but on pages with a crafted trojan.


[6] Microsoft DNS fix causes trouble for some

The Microsoft Corp. released a DNS fix in its patch slate for July, but the company seems to have problems just getting it to end users. Moreover, some users of the DNS fix have experienced additional difficulties.

So far, since Microsoft's DNS fix was issued on July 10, there have been two separate problems associated with its installation.


[7] H D Moore has NOT been owned

From the "half truths that journo's tell" file:

I've been following the Kaminsky DNS cache exploit issue closely since it was first announced - and no doubt so has everyone else in the security business. As such I was surprised to read a headline this morning that said that Metasploit founder H D Moore (and yes Virginia, there is a Santa Claus and I run Metasploit on a test machine too - who doesn't?) had been 'owned' (should've been p'wned I think) by the DNS flaw.

The story is not true - at least according to H D Moore who claims he was misquoted by the journalist in question.

"In a recent conversation with Robert McMillan (IDG), I described a in-the-wild attack against one of AT&T's DNS cache servers, specifically one that was configured as an upstream forwarder for an internal DNS machine at BreakingPoint Systems," H D Moore wrote in a blog post. "Shortly after our conversation, Mr. McMillan published an article with a sensationalist title, that while containing most of the facts, attributed a quote to me that I simply did not say. Specifically, `"It's funny," he said. "I got owned."


[8] SUBJECT: Microsoft SWI blog inaccuracies

As you know, 3 weeks ago I published my paper, "Microsoft Windows DNS Stub Resolver Cache Poisoning" (http://www.trusteer.com/docs/Microsoft_Windows_resolver_DNS_cache_poisoning.pdf),

simultaneously with Microsoft's release of MS08-020 (http://www.microsoft.com/technet/security/Bulletin/MS08-020.mspx). A day later, Microsoft's Secure Windows Initiative (SWI) team published their blog entry for MS08- 020 (http://blogs.technet.com/swi/archive/2008/04/09/ms08-020-how-predictable-is-the-dns-transaction-id.aspx).

Unfortunately, the SWI blog entry contains two serious mistakes. The first mistake is an inaccurate description of the PRNG used for the Microsoft Windows DNS client transaction ID. The second mistake is SWI's claim that "attackers cannot predict a guaranteed, known-next TXID exactly even with this weakness".

I contacted Microsoft about those mistakes, and while Microsoft did not refute my statements, they also refused to revise the blog entry. On one hand, I am inclined to tag this as a simple unwillingness on the side of the vendor to revise its materials and admit its mistakes. On the other hand, I cannot ignore the fact that the two mistakes, when combined, result in misleading the blog reader about the nature and the severity of the problem.

[...]

This is in stark contrast to SWI's claims. Furthermore, Microsoft did have the full paper (actually, a draft of it which contains all the relevant technical information) well before the SWI blog was published. So the problem here is not an issue of SWI not having access to the paper when they wrote their blog entry.


[9] Microsoft preps 133 patches for Windows DNS hole

Microsoft is working on 133 separate updates for the problem, Budd wrote.


[10] Microsoft DNS Server Attacks Continue

The concept enables malicious users to run code remotely under the system privileges generally granted to the DNS service itself.


[11] Microsoft: Patch for critical DNS flaw may be ready by 8 May

The cmopany has been under pressure to address the flaw, reported last week, since software that exploits it has now been widely disseminated, and criminals are beginning to use it in attacks.


[12] Attack code raises Windows DNS zero-day risk

At least four exploits for the vulnerability in the Windows domain name system, or DNS, service were published on the Internet over the weekend, Symantec said in an alert Monday.


[13] Cybercrooks exploiting new Windows DNS flaw

Cybercrooks are using a yet-to-be-patched security flaw in certain Windows versions to attack computers running the operating systems, Microsoft warned late Thursday.


[14] Microsoft's advisories giving clues to hackers

How's this for a new twist on the old responsible disclosure debate: Hackers are taking advantage of information released in Microsoft's pre-patch security advisories to create exploits for zero-day vulnerabilities.


[15] DNS security improves as firms tool up to tackle spam

Infoblox's survey found that the number of internet-facing DNS servers increased from 9m in 2006 to 11.5m in 2007, indicative of the overall growth of the internet. Percentage usage of the most recent and secure version of open-source domain name server software - BIND 9 - increased from 61 per cent to 65 per cent over the last year. Use of BIND 8, by contrast, dropped from 14 per cent in 2006 to 5.6 per cent this year. Usage of the Microsoft DNS Server on web-facing systems also fell, decreasing to to 2.7 per cent in 2007 from five per cent last year.


[16] Use of rogue DNS servers on rise

The paper estimates roughly 68,000 servers on the Internet are returning malicious Domain Name System results, which means people with compromised computers are sometimes being directed to the wrong Web sites — and often have no idea.


[17] New shield foiled Internet backbone attack

ICANN has yet to determine the exact techniques used in the February attack. The incident will be discussed at a meeting of DNS root server operators later this month, the organization said.


[18] Zombie botnets attack global DNS servers

Hackers launched a sustained attack last night against key root servers which form the backbone of the internet.

Security firm Sophos said that botnets of zombie PCs bombarded the internet's domain name system (DNS) servers with traffic.

"These zombie computers could have brought the web to its knees," said Graham Cluley, senior technology consultant at Sophos.


[19] EveryDNS, OpenDNS Under Botnet DDoS Attack

The last time the Web mob (spammers and phishers using botnets) decided to go after a security service, Blue Security was forced to fold and collateral damage extended to several businesses, including Six Apart.


[20] Homeland Security sees cyberthreats on the rise

To test the nation's response to a cyberattack, the Department of Homeland Security plans to hold another major exercise, called Cyberstorm II, in March 2008, Garcia said. A first such exercise happened early last year.


[21] Perspective: Microsoft security--no more second chances?

As if Homeland Security Secretary Michael Chertoff didn't have enough on his plate.

Not only has he had to deal with Katrina and Osama. Now he's also got to whip Steve Ballmer and the crew at Microsoft into shape. If past is prologue, that last task may be the most daunting of all.


[22] U.S. cyber counterattack: Bomb 'em one way or the other

If the United States found itself under a major cyberattack aimed at undermining the natio's critical information infrastructure, the Department of Defense is prepared, based on the authority of the president, to launch a cyber counterattack or an actual bombing of an attack source.


[23] US plans for cyber attack revealed

Comments

Recent Techrights' Posts

European Patent Office (EPO) Series: Temporary Public Office or Permanent Personal Feather-Bed?
there are no visible signs that the Administrative Council has the slightest interest in contemplating a change in leadership at the EPO
Brigading Against Women - Part IV - Death Threats, Threats to Women, and Threats for Pointing Out, Correctly and Based on Hard Evidence, That Garrett and Lozza Talk to Each Other About Me Every Year (for 4 Years)
Brett Wilson LLP too is a toxic manosphere
Making Oneself Obsolete With Slop
Dr. Lemire also puts on display a degree of hypocrisy
 
Gemini Links 26/09/2026: Computer Cases Dreary, Web Drowning in Botspam
Links for the day
Reform UK auditor: Electoral Commission accounts, Companies House accounts, a going concern or not?
Reprinted with permission from Daniel Pocock
More GAFAM Layoffs at Apple, Second Time in Weeks (Silent Layoffs Silently Target Older and "More Expensive" Staff)
How many layoffs happen at Apple silently and go unreported or very scarcely reported?
Gemini Links 26/09/2026: Rant About Slop Ruining Crafts (Drowning the Signal With Plagiarism) and "Going Mechanical"
Links for the day
Links 26/09/2026: Microsoft Says Notification Data Breach/Surveillance Hole There by Design, EU Rapidly Dumping Microsoft for Digital Sovereignty
Links for the day
The Former Linux News Site ostechnix.com is LLM Slop
Please do not link to sites that promote and/or spread slop
Links 26/09/2026: Volkswagen Recalling ~50,000 Cars, US Attacks Its Own Media
Links for the day
Brigading Against Women - Part III - Racism Looms Large, Not Just Sexism
threats from a racist
Microsoft CEO Calls Layoffs "Streamlining" and Says Microsoft Layoffs Are "Great to See"
The lack of honesty here is only to be expected from Microsoft
Media silence deafening as Reform UK on brink of administration
Reprinted with permission from Daniel Pocock
Gemini Links 26/09/2026: Travel, Group Insurance Death Spiral, Stargazing, and Lagrange Meets LLM Slop
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Friday, September 25, 2026
IRC logs for Friday, September 25, 2026
Longtime Symbol of Microsoft's XBox Franchise, Halo, Down to Barely 20 People
The purge is huge, far bigger than submissive media cares to point out
EPO Meeting Ran Out of Time to Discuss the Scabs ('Young Professionals')
EPO staff representatives in The Hague meet a member of the 'cocaine cabinet'
The Register MS Promotes Slop for Banned Companies That Put Chinese Back Doors in Things, "AI" Mentioned 37 Times in One Page!
taking money from the undemocratic state and its surveillance outfits
Microsoft Attacked European Courts and Jurists, Now Europe Dumps Microsoft
This is because GNU/Linux is technically better, but the political factors contribute to that as well
Julian Assange Ready to Talk More (After More Than a Decade of Arbitrary, Unjust Confinement)
Two years ago, upon his release, his wife said he'd need some time off before properly or fully returning to the public eye
IEEE Tribute to Richard Stallman, Michael Tiemann, Linus Torvalds, Larry Augustin, Eric S. Raymond, Bruce Perens, Frank Hecker and Brian Behlendorf (Revolution OS Showing)
Live shortly
Winding Up Racists
What happens next shall be interesting
Links 25/09/2026: Selling Rogue, Defective Bots as "Agents" Results in PR Fiasco and Breaches; Russian 'Hybrid Attack' and "How Russia Evades Sanctions"
Links for the day
Gemini Links 25/09/2026: Arvelie Calendar, 44net, Pebbles, and Building the Bagel Concert Finder
Links for the day
A Microsoft Lunduke OS (LCOS) is Not Even in Top 100 in DisroWatch, Microsoft Lunduke Just Games the Numbers Like Linspire Did (and Got 'Banned' for It)
Linspire used to send people to 'its' DisroWatch page to make the illusion of popularity
Large Wave of IBM PIPs, the RAs Wave Comes After 'Low-Hanging' Fruit (Families) Disposed of
PIPs are the new RAs
Links 25/09/2026: Carcinogen Atrazine Pollutes Americans' Bodies, "Donald the Deadbeat Does Diesel", and Anger Over Data Centres Grows
Links for the day
Theory That Microsoft Cheapens Its Workforce to Push Workers Out on Their Own (Theory Advanced by Insider)
people work longer hours for less, i.e. their hourly salary is decreasing
Daniel Pocock Makes It Into Mainstream Media Again (Going After Racists)
American bigots funding blatant and shameless racists here in the UK
Tackling Racism in the United Kingdom (Racism Funded by Americans) Using the Courts
We'll talk about racism my wife and I experienced in the events leading up to litigation
Another Woman (or Women) Has Just Run Away From Brett Wilson LLP (After Barely a Month!), the Hired Guns of Garrett and Graveley (Microsoft)
They call this phenomenon "death spiral"
SLAPP Censorship - Part 200 Out of 200: Will GNU Boot Undo the Technical Damage Caused by Microsoft and Garrett? (And Garrett's Litigation Allies From Microsoft)
Today we publish the final part of this series
US Government Sites Can Now Totally Ignore Mozilla Firefox Users or Users of Firefox Derivatives
Firefox, now at 1.1% in the US (based on American government sites), has sunken to the point of no return
Things Not to Measure in Quantity Alone
More patents do not beget greater innovation
Even Microsoft Boosters Start to Doubt XBox Will Exist (It's Being Phased Out, Just Not "Officially")
This is how to phase out a business unit without officially saying so (as it might alarm investors)
Omarchy is Built on the Idea That Slop is Desirable (It's Not)
They call bots and plagiarism "agents" and "training"
IBM is Shrinking Very Fast (Silent, Unannounced Layoffs)
IBM and Microsoft both avoid WARN notices by compelling staff to leave or silently removing them with some NDA
In Some Parts of Microsoft 50% of All Staff Subjected to Layoffs, Media Pretends Only 0.1% of Staff Are Removed
This really says a lot about the state of today's so-called 'media'
SLAPP Censorship - Part 199 Out of 200: An American Burden on the British Legal System
A year ago (October 2025) the head of media (Jointly in Charge of the Media and Communications List), the judge in the Garrett case, said that this case was a waste of the court's money
EPO Management Wants Everything to be Done in Microsoft Spyware
In reality, this management should be ousted for normalising cocaine at the Office
Criminalising Opposition to Fraud
slop causes social issues
The Register MS Does Not Properly Flag Its SPAM About Slop
Signs of desperation
Gemini Links 25/09/2026: Ljubljana, Tanana River, and Curse of Slack
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Thursday, September 24, 2026
IRC logs for Thursday, September 24, 2026
Supporters of winding-up process staking claims against Reform UK Party (CR-2026-007405)
Reprinted with permission from Daniel Pocock
Winding-up petition leaked before service on Reform UK Party Limited / Nigel Farage
Reprinted with permission from Daniel Pocock
Gemini Links 24/09/2026: Laziness, Outdoor Seating, "AngelNova’s Interview Malware and Its North Korea Connection"
Links for the day
Links 24/09/2026: Slop "Linked to Disturbing Culture of Sexual Assault"; "Zelensky Warns Russia’s War Will Expand if It Is Not Ended Soon"
Links for the day
Winding-up petition served on Reform UK Party Limited (Nigel Farage)
Reprinted with permission from Daniel Pocock
Appliances Should be Dumb
Any "Smart Home Appliance" is basically a thing that does not last long, does not work as advertised, and is generally unfit for purpose
SLAPP Censorship - Part 198 Out of 200: It Sounds Like Garrett is Now Sending People to Silence Critics (Including His Own Spouse)
This week Garrett is having a somewhat karmic experience
Links 24/09/2026: Slop Contaminating KDE, Slop-Focused Data Centres Have Severe Environmental Impact
Links for the day
SLAPP Censorship - Part 197 Out of 200: Garrett Became So Poor That He Wants Others (in Another Continent) to Pay for His Own Legal Work Being Faulty
They lie to courts
The Register MS Has Become a Slopfest
This is the behaviour of a perishing publisher
Gemini Links 24/09/2026: Requiem for a Season, Philosophy, Rube-Goldberg Machine, ROOPHLOCH 2026, and Git over Gemini
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Wednesday, September 23, 2026
IRC logs for Wednesday, September 23, 2026