Bonum Certa Men Certa

NSA Shows Why We Should Abandon All Proprietary Software and Verify Trust

Without source code of all levels/layers of the software trust just cannot be established
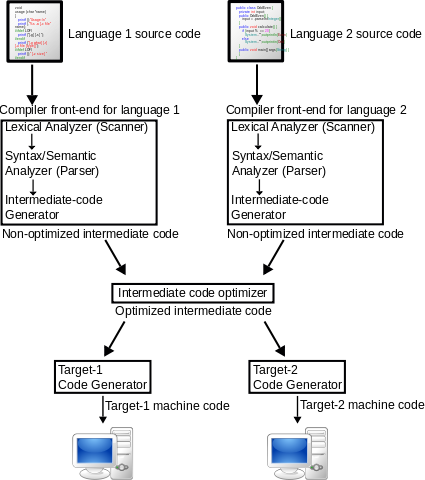
Compiler


Summary: Proprietary software can never be secure and back doors inside of it can be assumed (unless proven otherwise), based on some of the latest NSA leaks

THE NSA is a criminal operation, so we expect it to work with other criminal operations. Microsoft and the NSA collude to make the world a less secure place, enabling espionage with Windows (Stuxnet for example) and providing video/audio surveillance in people's own homes without any warrants. Microsoft is about lawlessness is the same way the NSA is. The law of "rule" supersedes the rule of law.


Some say that the Windows-centric Stuxnet is the "world's first true cyber-weapon", but that is not true. History aside, to put it as IDG put it: "Stuxnet's creators recognized they had built the world's first true cyber-weapon and were more interested in pushing the envelope of this new type of digital warfare than causing large-scale destruction within targeted Iranian nuclear facilities, a study shows.

"In an analysis released last week, Ralph Langner, head of The Langner Group and a renowned expert in industrial control systems (ICS), also refuted arguments that only a nation-state had the resources to launch a Stuxnet-like attack. Assailants with less ambition could take the lessons learned and apply them to civilian critical infrastructure, he said."

This was an example of overreach and violation of the law, enabled of course by Microsoft and Windows. GNU/Linux does not sell its users down the river the way Windows does.

Sadly, firms like White Source make a comeback with their FUD and they single out FOSS for security issues (here is the press release). This is not acceptable because they totally ignore the much bigger threats, as above (where security issues are there by design).

The White House is at war against FOSS geeks and other phantom enemies [1,2], where the logic is something along the lines of, if we don't control it (we as in the government), then it's a threat to national security. While it seems clear that a brute force attack is the Achilles Heel of FOSS [3,4,5] and Google keeps improving security of FOSS projects like Android [6,7,8,9.10] and others [11,12], the logic followed by the likes of White Source and White House is that if something proprietary keeps its flaws (or back doors) secret, then it's secure and we should not pay attention to real security. Again, this is simply not acceptable.

The head of the Linux Foundation recently said that FOSS is safer, and Linux is more secure than any other OS [13]. Mikko Hypponen seems to agree with him [14] and despite some new known flaws in Red Hat software [15,16] (transparency makes weaknesses visible) we should remember that lack of knowledge about something does not mean it's not there. Just because we cannot easily see back doors in proprietary software doesn't mean they're not there (some groups of people know they're there and they exploit them silently). If Europe is serious about cyber security [17], then it should dump all proprietary software (back doors-friendly software) as soon as possible. Given everything we now know about the NSA, ignorance and uncertainty are no longer an excuse. A Dutch source has just revealed that the NSA cracked 50,000 computer networks. The evidence is overwhelming. Stuxnet is peanuts next to that. ⬆

Related/contextual items from the news:


  1. How Antisec Died
    Depending on when one asked, Antisec was generally between 8-10 people, with a solid core of about six. Not all of them were comfortable with talking to me, and certain ones were designated to communicate with press. I was never entirely sure who was in or out at any particular time — it was a fluid group. I never knew all the nicks. I talked repeatedly with five of them, including Sabu.


  2. Bizarre Online Gambling Movie-Plot Threat
    This article argues that online gambling is a strategic national threat because terrorists could use it to launder money.


  3. Huge horde of droids whacks code box GitHub in password-guess attack


  4. GitHub resets user passwords following rash of account hijack attacks
    GitHub is experiencing an increase in user account hijackings that's being fueled by a rash of automated login attempts from as many as 40,000 unique Internet addresses.
  5. Google extends its proactive Patch Reward Program to include Android Open Source Project, Web servers, and more


  6. Google adds Android Open Source Project to Patch Rewards program
  7. Google expands Patch Rewards Program
  8. Google extends open source bug bounty programme to Android and Apache


  9. Android now part of Google’s Patch Reward Program


  10. Google adds Android and Apache to open source security rewards programme
    Google has extended its Patch Reward Program to include a raft of new platforms and technologies including its own Android system as it looks to improve the securiry of open source software.

    The firm announced an overhaul to its security patch policies last month, offering white hats up to $3,133 for fixes.


  11. Experts applaud Google completion of SSL certificate upgrade
    Step up to 2048-bit keys optimizes balance between protection of company services and maintaining performance


  12. Pinkie Pie and His Google Exploits: The Legend Grows
    Pinkie Pie returned in 2013 for the desktop Pwn2Own event operated by Hewlett-Packard's Zero Day Initiative (ZDI), taking aim once again at Google. This time, it was Google's Chrome browser running on Chrome OS. Pinkie Pie's effort landed him another $40,000 in award money for the discovery and reporting of what turned out to be a trio of flaws, including one buried deep within the Linux kernel. Chrome OS is a Linux-based operating system that Google uses on its Chromebook notebooks.

    But wait. There is still more.

    Just this week in Japan at HP's Mobile Pwn2Own event, the legend of Pinkie Pie grew as the My Little Pony-loving security researcher once again demonstrated previously unknown zero-day flaws in Google's Chrome. Pinkie Pie was able to pwn Chrome on both a Nexus 4 as well as a Samsung Galaxy S 4 smartphone. This time, Pinkie Pie pocketed $50,000 for his efforts.


  13. Linux chief: ‘Open source is safer, and Linux is more secure than any other OS’ (exclusive)


  14. Mikko Hypponen: Open Source Software Will Make the World More Secure
    Open source software can be one answer to combating the global surveillance of innocent citizens, said security expert Mikko Hypponen in his keynote last week at LinuxCon and CloudOpen Europe in Edinburgh.


  15. Hackers actively exploiting JBoss vulnerability to compromise servers, researchers say
    Attackers are actively exploiting a known vulnerability to compromise JBoss Java EE application servers that expose the HTTP Invoker service to the Internet in an insecure manner.


  16. Red Hat: 2013:1521-01: python-django: Moderate Advisory


  17. European businesses urged implement anti-cyber security systems
    The European Cyber Security Directive, which proposes that European businesses have a legal obligation to ensure they have suitable IT security mechanisms in place, is soon to be enforced in the UK.


Recent Techrights' Posts

Birss Replaces Vos in UK's High Court, LLM Slop Plagiarism a Contentious Issue
Only days ago we mentioned Sir Geoffrey Vos in relation to lobbying for LLM slop
Despite the Mass Layoffs Microsoft's Debt Soared by 5.1 Billion Dollars in Just 3 Months
This is why Microsoft asks 60,000 workers to leave
What Linus Torvalds Told Me Two Decades Ago
It seems like he was eager to distinguish himself from the "elders" of FSF [...] For anything "revolutionary" to happen in the sciences one must accept the risk of living in poverty like Tesla (the person, not the right-wing fanatics) and Torvalds isn't too old to "cause a stir"
 
Intercontinental Brigading - Part XXIV - It's an Inherently American Issue and American Elections Are at Risk From Restricted ('Secure') Boot and LLM Chatbots (Disinformation at Scale)
We'll focus a lot on US elections in the coming days
"Early Retirement" (Silent Layoffs) for Everybody Except the Executives
Some will stick around even past 70
Gemini Links 30/10/2026: Solar MiniBBS, Kubernetes With FreeBSD, "Sysadmin Day"
Links for the day
Microsoft Layoffs Far Worse Than the Media Tells (Microsoft Spin Laundered as "Reporting")
Some people are made to "retire" and sign an NDA to make it seem like a happy ending and mostly consensual retreat
Links 30/10/2026: Google Crashes on Slop Disappointment and GAFAM's "Data Center Blitz Is Burning Through Cash and Scaring Wall St."
Links for the day
Fake 'Articles' in The Register MS Concerning "AI"
We don't suppose The Register MS will be around for much longer after this bubble pops
GNU/Linux as a Free Software Platform is More GNU (and GPL) Than Linux
GNU predates Linux by nearly a decades and it was born to tackle injustices
Who Or What Are Security Professionals/Experts?
Companies like GAFAM are willing to tolerate cheaters because those companies themselves are cheats
Intercontinental Brigading - Part XXIII - What Garrett Did Puts Elections at Risk (Also in His Own Country, Where a Dictator Trusts Only Machines That 'Support' Him)
UEFI 'security' is only as trustworthy as its ferocious boosters
Gemini Links 30/10/2026: RIP Patrick Stewart and Amp Integration
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Thursday, October 29, 2026
IRC logs for Thursday, October 29, 2026
The Metric is Not the Mission
"Passing Thoughts" by Andy
More Than 5 Years Have Passed Since Official Release of Vista 11 and in the US It's Measured as Only 3 Times Bigger Than GNU/Linux on the Desktop/Laptop
If mobile is culled from the statistics, then GNU/Linux is somewhere near 11%
It's About Intention, Not Attrition, at Microsoft
Microsoft does in fact aim to push many workers off the cliff
The Next 50 Years of Emacs (and GNU)
GNU's founder made the widely used editor, GNU Emacs
Links 29/10/2026: Microsoft-Connected and Funded Openwashing at FOSDEM, Tragedy in Spain
Links for the day
Gemini Links 29/10/2026: London, Worcestershire, and Robot Exclusion Protocol
Links for the day
The Register MS is Publishing Spam About "AI" for HP, Sponsored by HP, Even Composed by HP
Or "HPE" as they choose to call themselves (with the hype of "enterprise")
Links 29/10/2026: Anthropic Still Sued Over Copyright Infringement (Plagiarism Isn't "Training"), Elon Musk Openly Admits He Helps Putin Crush Ukraine
Links for the day
Intercontinental Brigading - Part XXI - Techrights Was Right, So Why Was It Punished by Lawfare While the Culprits Walk Away Scot-free?
Techrights did a public service, cautioning about real risks to the public, but the people who caused the problems walk away scot-free
Intercontinental Brigading - Part XXII - Still "Radio Silence" From "Restricted Boot" Perpetrators (After Techrights Proven Right Again)
Maybe when they sober up they'll say something...
'Secure' Boot Is Not Secure, Here Are News Reports About the Latest Evidence
We'll be linking to this page in the future as evidence of the catastrophe
No, Microsoft Isn't Doing Well (It Has Struggled for a Long Time)
Microsoft isn't growing, the shares are a Ponzi scheme of sorts
What Makes Techrights a Community
Communities can accomplish a lot. They cannot be "bought" and "sold", they're based on trust, mutual respect, and shared ideology.
Linux Links 29/10/2026: Refractor Stargazing and Making Better Use of RAM in Linux
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Wednesday, October 28, 2026
IRC logs for Wednesday, October 28, 2026
Project Glasswing and PHP2Shell vulnerability
by Akira Urushibata
Turning Point for the Slop Industrialists
First, a lot of people who work on "hey hi" at Microsoft (no matter the buzzword or brand, e.g. "copilot") are impacted
Links 28/10/2026: Slop Bubble Pops in China, Rocky Linux Creator Becomes Slopper, Openwashing by the Slop Pushers Explained
Links for the day
Gemini Links 28/10/2026: Slop Plagiarism Considered a "Weapon", "Completely restored HTML interface to the Orbital Fox mailing list"
Links for the day
The Corrupted Corporate Media is Spinning Massive Microsoft Layoffs as "Investment in AI" Instead of Evidence That "AI" Nonsense is Catastrophic
Microsoft asking 30% of its staff to leave is a sign of bubble
Links 28/10/2026: "Rest of World Faces Prospect of Shutting Down" and Robert Reich Says "Musk Wants Me Imprisoned"
Links for the day
Gemini Links 28/10/2026: Cold Outside Again and Maths
Links for the day
Intercontinental Brigading - Part XX - Restricted and Moot, or How 'Secure Boot' Turns Out to be a Disaster (Again) This Week
It already has a history of breaking/bricking servers
100 Years of IBM Racism
GAFAM is not about "diversity" or "equity" or whatever. It's a greedy, money-making venture, even if they appoint CEOs of colour
Racism at Microsoft
Microsoft tribalism has an element to it aside from corporate allegiance
Intercontinental Brigading - Part IX - Literature About Malignant Narcissists in America Silencing the Press
There's a price for criticising abuses
Compelling Examiners at the European Patent Office to Fake "Growth" (in Patent Monopolies) Using Slop and Sloppy Processes
The agenda of management is likely illegal and the methods likewise
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Tuesday, October 27, 2026
IRC logs for Tuesday, October 27, 2026