Bonum Certa Men Certa

EPO and Microsoft Collude to Break the Law -- The 'Smoking Gun': Hard Evidence That the EPO Has Been Lying About GDPR Compliance

What the EPO says:

EPO CA-20-19 page 49 of 88

Summary: The EPO's Annual Reports of the Board of Auditors help show that the cronies of Benoît Battistelli have been lying all along about GDPR compliance; António Campinos is, as expected, just another one of those Battistelli cronies, in effect passing EPO funds into a gambling black hole and overseas violators of everybody's privacy

We have managed to track down copies of the "audit reports" which allegedly confirm a close alignment between the EPO's data protection framework and the GDPR.


As far as we have been able to work out, the "audit reports" that the EPO refers to in its data protection "puff pieces" are the annual reports of the supposedly independent Board of Auditors (warning: epo.org link). One of these "independent" auditors is Battistelli's old crony from the INPI, Frederic Angermann.

" One of these "independent" auditors is Battistelli's old crony from the INPI, Frederic Angermann."Anyway, the annual audit report is usually issued as Administrative Council document no. 20 at the end of April or beginning of May each year.

So for 2020, the document is numbered CA/20/20 [PDF].

For 2019 it is CA/20/19 [PDF] and for 2018, the reference number is CA/20/18 [PDF].

"From this it can be seen that the the annual reports of the Board of Auditors just parrot the party line of EPO management..."We've made local copies as we want this to last and remain unchanged, just in case something mischievous was to happen at the EPO's end. As happened in the past...

The documents are publicly available via the official webpage of the Council (warning: epo.org link) and can be found using the search keyword "auditors".

The first mention of GDPR is in the 2018 audit report, CA/20/18, on page 6 of 81:

42) As of 25 May 2018, a new, uniform General Data Protection Regulation (GDPR) on data privacy will apply across the European Union (EU) to all organisations collecting and/or processing data from EU residents. 43) On July 2017, the President issued a task force with a mandate to assess the potential impact of this new EU GDPR on the EPO's current data protection guidelines. 44) It is noted that the EPO's current data protection guidelines are relatively closely in line with the new GDPR. However, an action plan is in place to address the potential impact of the GDPR on the EPO.
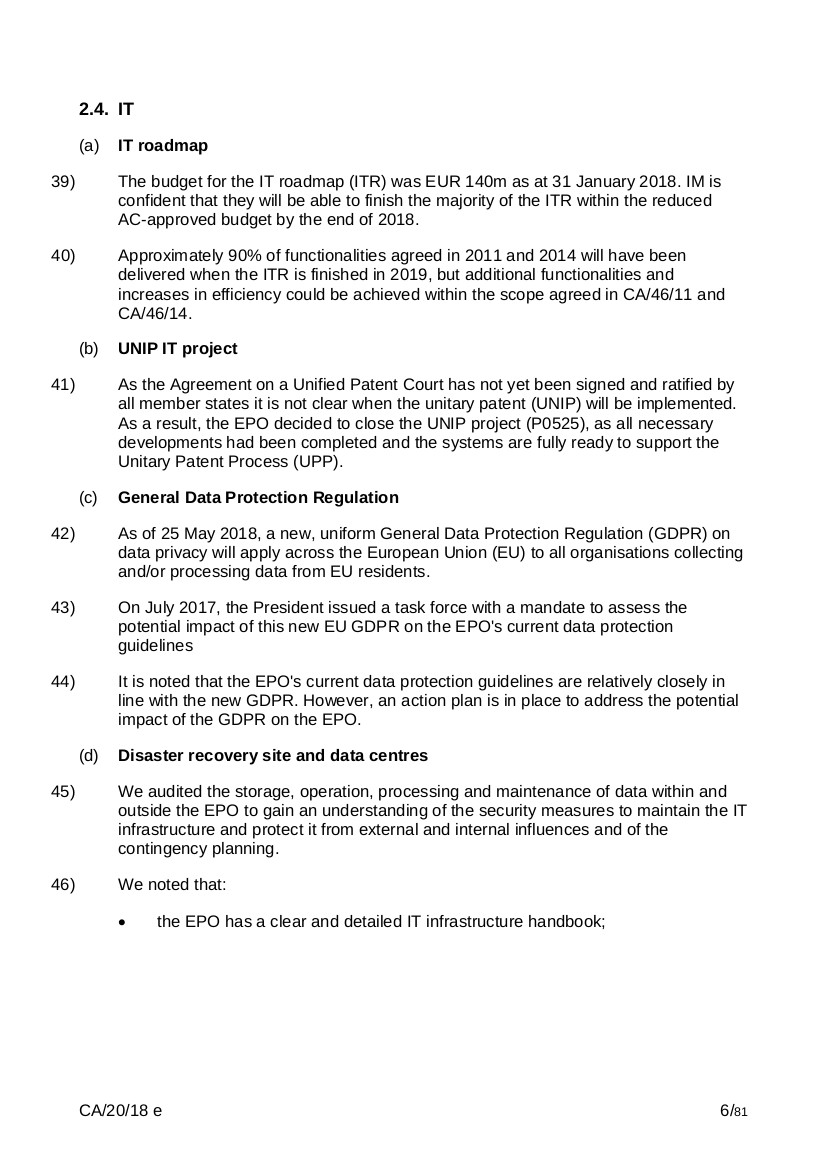

EPO CA-20-18 page 6 of 81

The 2019 audit report, CA/20/19, contains the following statement:
259) The new European General Data Protection Regulation (GDPR) has been in force since 25 May 2018. Even though the EU regulations do not directly apply to the EPO as an international organisation, basic principles have been implemented, as European citizens' data is processed at the EPO.


It then goes on to talk about a the implementation of a "data protection register to record all the processing operations carried out on personal data" which can be accessed by EPO employees on the EPO intranet. It is not accessible to external data subjects but external parties can make a data subject access request "thus ensuring the right to information". This is followed by a recommendation that data protection register needs to be updated and to be completed in order to ensure that all relevant information is available.

The report then states that the EPO's IT department, referred to as IM (= Information Management) is "only involved in the GDPR analysis on a high-level basis" and that IM does not prepare the necessary implementation, such as deletion concepts.

This section of the report concludes with a recommendation to include IM much more in the GDPR evaluation "to ensure that technical and organisational measures are addressed adequately. Additionally technical solutions need to be evaluated."

The 2020 audit report, CA/20/20, contains a section entitled "Analysis of implementation of GDPR requirements in the HR area" on page 7 of 89. According to this:

41. Since the Office, as an international organisation that does not fall under the EU regulations, is not subject to the General Data Privacy Regulation (hereinafter: "GDPR"), the internal "Guidelines for the protection of personal data" were developed and introduced by the Office with the latest revision in 2014. The abovementioned guidelines are very close to the requirements of the GDPR and Regulation (EU) 2018/1725 and as such are to be implemented and followed by the Office.
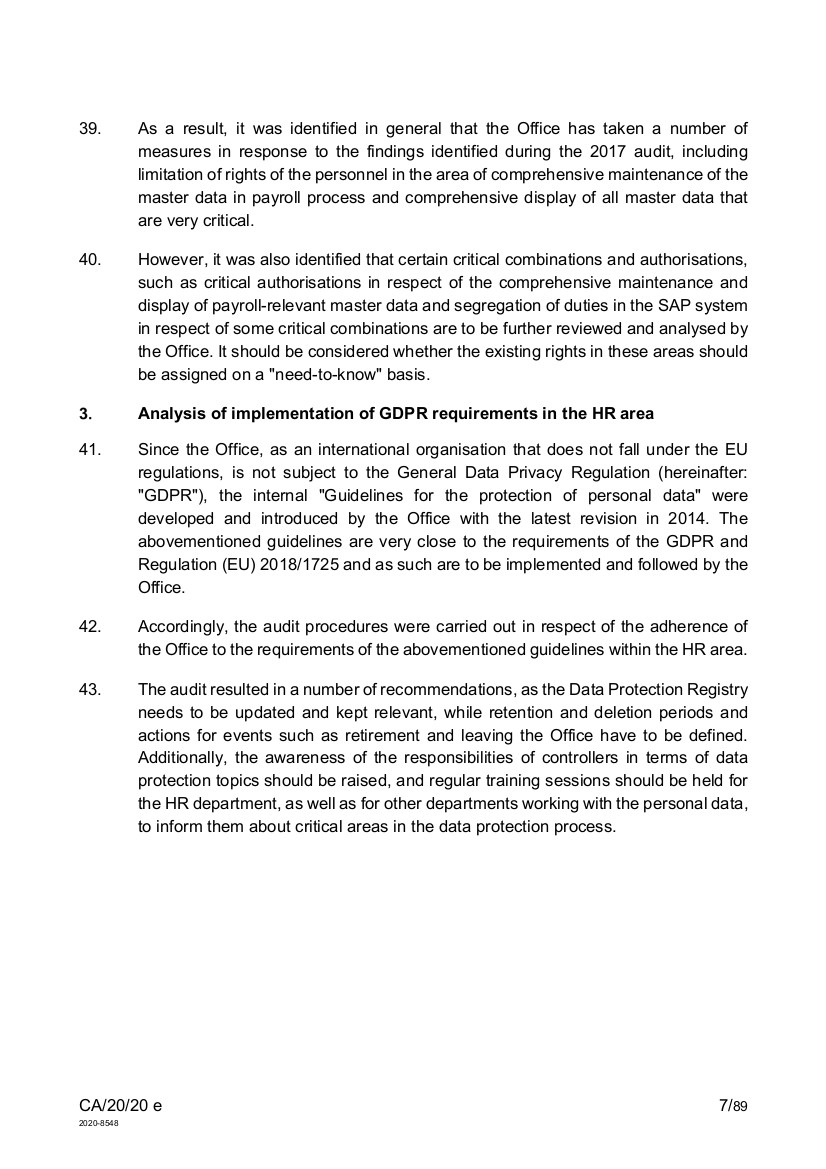

EPO CA-20-20 page 7 of 89

There are two short paragraphs explaining that "audit procedures were carried out in respect of the adherence of the Office to the requirements of the above-mentioned guidelines within the HR area" and that the audit "resulted in a number of recommendations", such as the need to update the Data Protection Registry and to define retention and deletion periods and actions for events such as retirement and leaving the Office.

"There hasn't actually been any independent audit of the EPO's data protection framework to determine the level of GDPR compliance."Additionally, it recommends that "the awareness of the responsibilities of controllers in terms of data protection topics should be raised, and regular training sessions should be held for the HR department, as well as for other departments working with the personal data, to inform them about critical areas in the data protection process."

From this it can be seen that the the annual reports of the Board of Auditors just parrot the party line of EPO management according to which "the EPO's current data protection guidelines are relatively closely in line with the new GDPR" (CA/20/18) and "the internal 'Guidelines for the protection of personal data' [which] were developed and introduced by the Office with the latest revision in 2014 ... are very close to the requirements of the GDPR and Regulation (EU) 2018/1725" (CA/20/20).

There hasn't actually been any independent audit of the EPO's data protection framework to determine the level of GDPR compliance.

All that we have are bald assertions of GDPR compliance by EPO management which have been rubber-stamped by the auditors without further ado.

"All that we have are bald assertions of GDPR compliance by EPO management which have been rubber-stamped by the auditors without further ado."Given that EPO management claimed at the time of adoption of the EPO's internal "Guidelines for the protection of personal data" in 2014 that they were closed aligned to the earlier EU Regulation (EC) 45/2001, it remains to be explained how these same Guidelines could now manage to be compliant with the GDPR which was not adopted by the EU until 2016 and entered into force in 2018.

Of course it's complete nonsense but as long as nobody actually goes to the trouble of carrying out an independent audit who's going to notice anything? ⬆

Recent Techrights' Posts

Intercontinental Brigading - Part XVI - The Faustian Pact That Irritates Hired Guns is Still a Distraction From the Serious Harm Done by Their Clients to GNU/Linux Users (Notably Plagiarism and Back Doors)
We'd rather talk about the harms caused
Intercontinental Brigading - Part XV - Annualised Consequences for Opposing Microsoft Back Doors in Linux Since 2012
a roundup of what we got from GGG
In Reporting, Timing is Everything
If you keep calling people "paedophiles" when you yourself are connected to paedophiles (or are a paedophile), you're attracting a lot of unwanted attention to yourself
 
This is How Microsoft Ends (Over a Quarter of the Company Now on the Chopping Block)
Microsoft has quit pretending
Search Without Encryption for Legacy Systems (Permacomputing) and Full Backward Compatibility
At your own risk
Shift to the Lula (Left)
Lula is a friend of Free software and ODF
More Stories and Material Than We Can Publish
We're gaining or have amassed material faster than we manage to publish
European Patent Office Takes From the Poor to Give More to the Rich
The "pension schemes are overfunded at 120.5%"
Links 26/10/2026: China’s Communist Party Plenum and Aleksandar Vucic Concedes Defeat
Links for the day
Links 25/10/2026: Microsoft Layoffs and Cuts, Luiz Inácio Lula da Silva Wins Election
Links for the day
Gemini Links 26/10/2026: Brazilian Politics and Leaving Bear Blog
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Sunday, October 25, 2026
IRC logs for Sunday, October 25, 2026
Another Form of Microsoft Silent Layoffs: Workers That 'Expire'
When the media becomes a lapdog, not a watchdog, false narratives gain traction
Carte Blanche for GPL Violations 4 Days Ago (by Torvalds)
Slop disclosure is no longer required for the Linux Kernel
There Are No Women That Are Kernel Developers Sent by Corporations Which Claim to Champion Diversity
As noted the other day
Sites with "Linux" in Their Name Cannot Slop and Retain Readers
if they write about "linux "(or "Linux") using LLMs they will be caught, then shunned
At Microsoft, the Silent Layoffs Impact Executives Also
Microsoft hid the real story of Helen Chiang
Linus Torvalds Defected to Enshittification
Linus Torvalds is betraying a generation of high(er) standards
Links 25/10/2026: TMZ Revisits Epstein's Connections to Bill Epsteingate, "Italy Hit by New Cost of Living Protests"
Links for the day
Microsoft’s Spin About Mass Layoffs and Shutdowns: They "Never Should Have Existed"
Microsoft-sponsored spin
It's Slop
Maybe we'll exclude It's Slop from our curation. It's a Linux Foundation outpost of sorts, an apologist of sloppy code and plagiarism.
Intercontinental Brigading - Part XIV - Six Years of Learning Irish, But the Real Issue Was Microsoft-controlled 'Secure' (Restricted) Boot
Had I not opposed back doors in Linux, not of this would come about
Gemini Links 25/10/2026: Moana (2026) and OpenBSD Updates
Links for the day
The Netherlands Fast to Adopt GNU/Linux, "Market Share" Rises to Two-Digit Value (on Desktops/Laptops)
It peaked at around 20% yesterday
DST Still Needs to Get Abolished
Get rid of DST, efficiency will improve and systems will become more reliable
PHP2Shell as Paid-for FUD Campaign (Intended to Help Sell Slop and Fake "Market Value" of Slop Pushers)
PHP2Shell considered overhyped [...] Remember all the paid-for hype regarding Mythos? What happened to all that?
Microsoft Sort of Tried to Sell XBox Piecewise (Offloading Microsoft)
XBox is in a morbid state
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Saturday, October 24, 2026
IRC logs for Saturday, October 24, 2026
Gemini Links 24/10/2026: Arch Linux Journey and Amin Bandali's Priorities
Links for the day
Bluewashing as a Form of Silent Layoffs
IBM will continue to shed off loads of workers while its debt climbs
Turning 20 in 2 Weeks and Upcoming Network Maintenance
That ought not interrupt our anniversary
Microsoft Shutdowns Accelerating, More Shutdowns Revealed (Not Connected to Gaming)
Silent layoffs disguised as "voluntary" "exits"
Links 24/10/2026: Microsoft Blackmail and Lingering Unrest in France:
Links for the day
Gemini Links 24/10/2026: From Bendigo to Kerang, Enshittification of Radio and Music in the UK
Links for the day
Red Hat Sinks With the Blue (IBM) Ship
As IBM's debt continues to soar so do the silent layoffs
Linux is Not Controlled by Linus (Torvalds)
Torvalds has become "90% marketing hype"
The "No Pain No Gain" Expectations in Publishing
Sometimes truth hurts; but that does not mean it mustn't be told
Intercontinental Brigading - Part XIII - Censorship by All Means Available in a Continent So Far Away, as 'Secure' (Restricted, Restriction by Microsoft) Boot Has a Crisis of Legitimacy
it's about America controlling sites and computers everywhere
Links 24/10/2026: Oligarchs Already Buy US Elections, GAFAM Front Group "EFF" Speaks of "Vulnerability Apocalypse"
Links for the day
Gemini Links 24/10/2026: Automobile Differential Tire Movement, Samsung Washer Woe, and Slop Scraping
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Friday, October 23, 2026
IRC logs for Friday, October 23, 2026