Summary: Mitchel Lewis, a former Microsoft employee, takes a look at Microsoft-connected or Microsoft-controlled 'think tanks' in 'task force' clothing
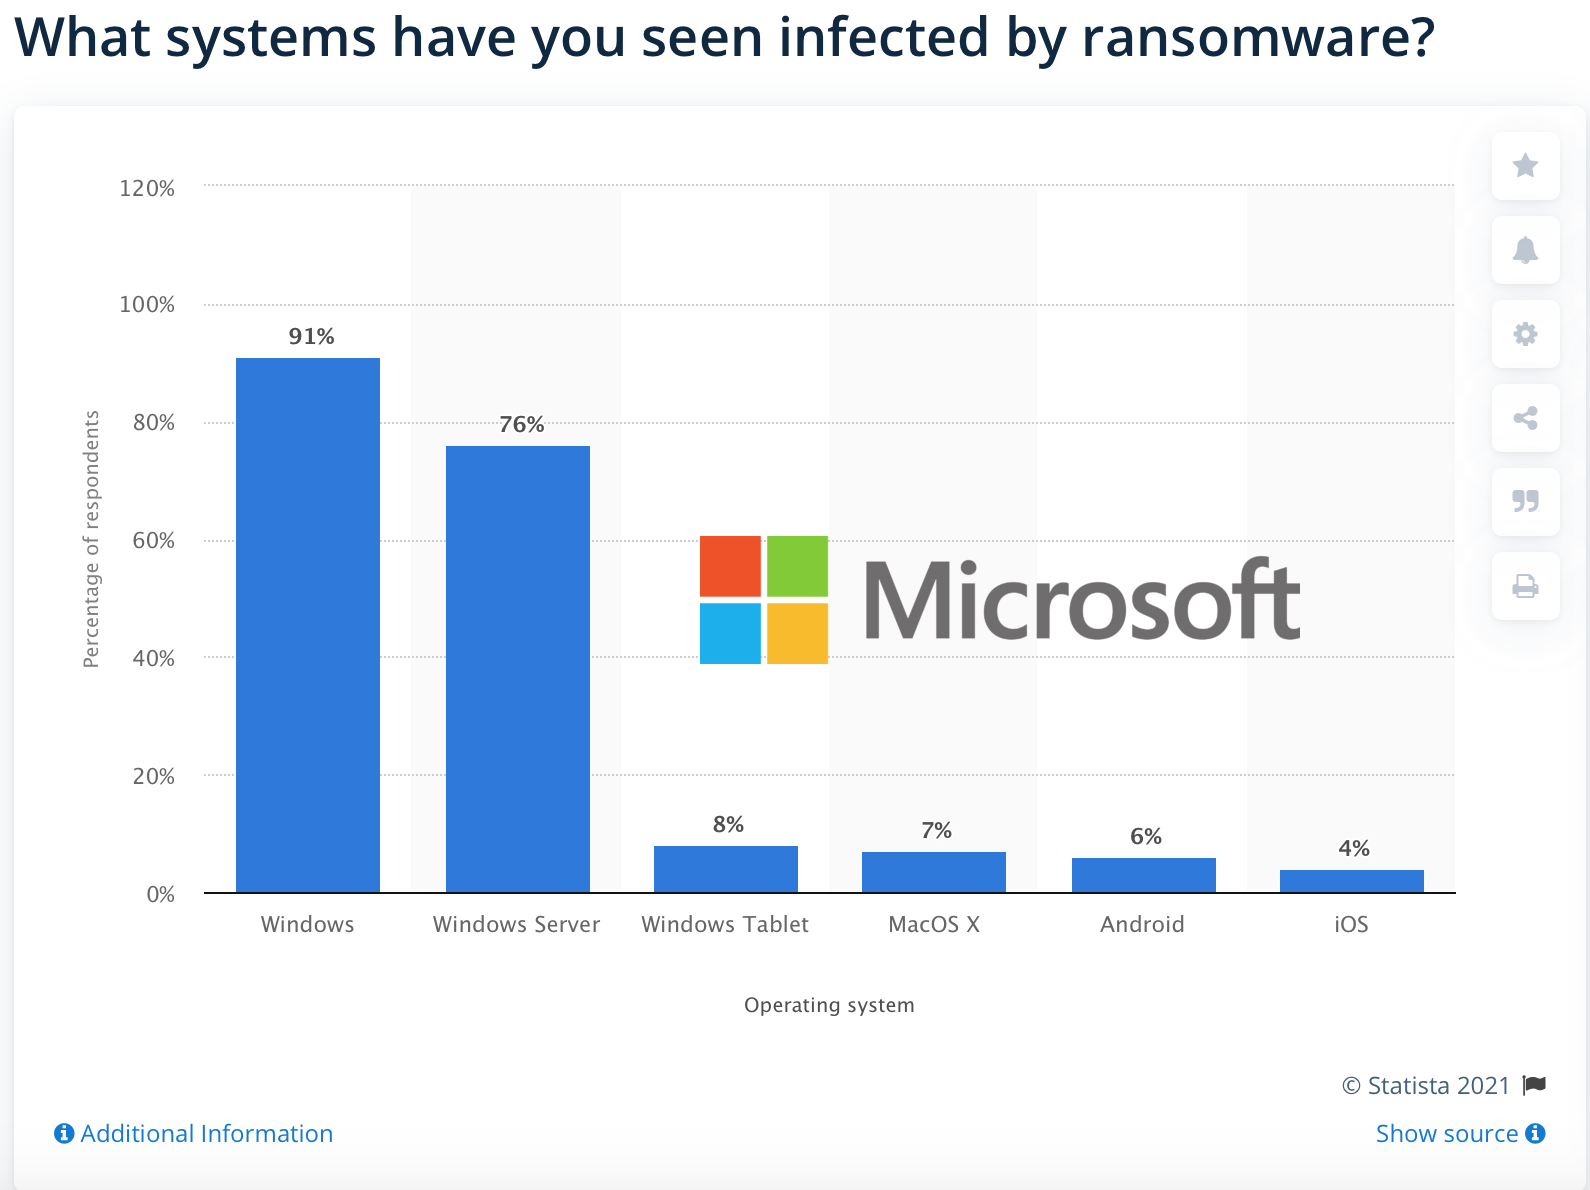
Although most platforms have had their flare-ups with ransomware, it’s well-known that Microsoft’s legacy architecture has a hyper-monopoly with respect to ransomware infections that consequently renders all other platforms into negligible outliers in comparison. In fact, there’s nothing in this world that Microsoft monopolizes better than ransomware attacks at the moment.
Depending on who you ask, anywhere from 85–99% of ransomware attacks occur on Microsoft architecture, often via well-known vulnerabilities. Because of this common denominator, most working within the ransomware space daily would find it supremely difficult gloss to over the vulnerability of Microsoft’s architecture as being a key component in the rising prominence of ransomware and this is especially true if they were asked to write an 80-page report on the matter.
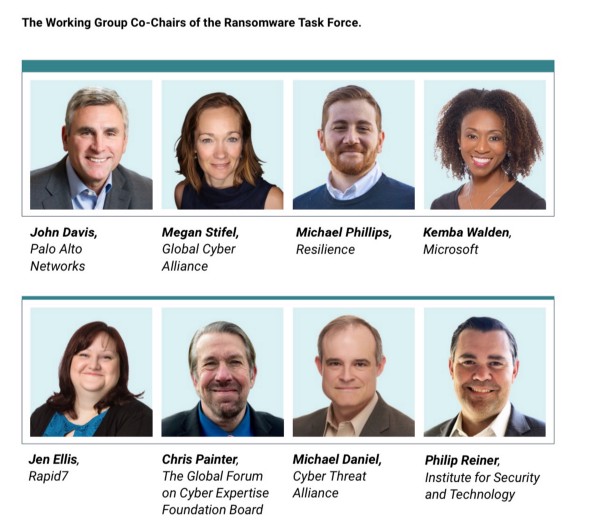
A “venerable” who’s who of the ransomware field.
Recently though, a team of more than 60 lawyers and supposed experts that no one has ever heard of before from software companies, cybersecurity vendors, government agencies, non-profits, and academic institutions came together with the Institute for Security and Technology, an institute that no one has ever heard of before, and achieved the irrational by developing a “comprehensive framework” attempting to tackle the modern threat of ransomware. To no surprise and in true Dunning-Kruger fashion whenever expertise is proclaimed, these experts managed to accomplish the unconscionable by overlooking Microsoft’s blatant complicity in the ransomware space and the fundamental importance of modern infrastructure in the face of IT security and prevention of ransomware in an 81-page report.
This wasn’t even a revelation in December for anyone with half of an ass in the field of assessing root cause.
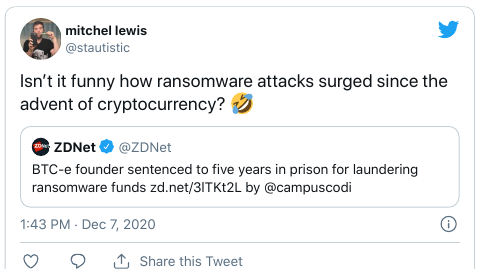
To be fair, the task farce rightfully highlighted the rise of cryptocurrency as a motivational force behind ransomware attacks and further dubbed ransomware to be a threat against our national security, this is nothing new; even my stupid ass has been talking about this for 6 months now. Many of their suggestions are relevant too and might help to some degree, but they’re reactionary and ancillary at best in comparison to an architectural shift away from Microsoft solutions; the single best preventative measure that a company can take to defend itself against various attacks plaguing industry throughout the world, ransomware or otherwise. Hell, their whole article only mentioned prevention 3 times.
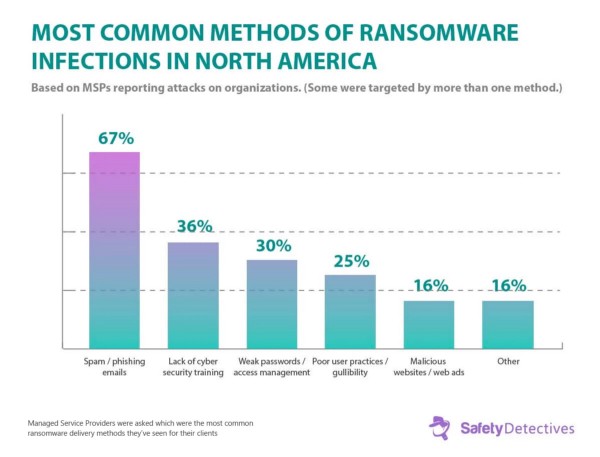
With the exception of Hafnium, most attacks are rudimentary at best and exploit well-known vulnerabilities throughout the Microsoft ecosystem and the ignorant companies refusing to mitigate these vulnerabilities in favor of convenience. More often than not, ransomware infections are a direct consequence of phishing campaigns, poor password complexity, poor lockout policies that embolden brute force attacks, poorly trained users, no MFA, no VPN, and admins ignorantly exposing RDP to the WAN, etc. All of which are fundamental no-no’s in the world of IT security that are amazingly easy to prevent and almost all of which are targeted exclusively at Microsoft cloud and server solutions hosted on-premise by their clientele. And a task force of supposed experts would have acknowledged this if they were actually experts in ransomware or IT security.
Given all of this, it seems as if Microsoft is just as much of a threat to our national security as ransomware itself; you can’t have one without the other. Although many of these attacks are preventable and much can be done to supplement Microsoft architecture to harden against said attacks, it’s becoming increasingly evident that it’s impossible for most teams to account Microsoft’s entire threat surface, ransomware or otherwise, and that it’s simply too complex, costly, and cumbersome for most IT staff to manage. As such migrating away from the Microsoft ecosystem entirely is the single most viable way to reduce your threat surface against ransomware and pretty much every other form of attack; the drastic reductions in IT ownership costs and improved employee morale are nice too I hear.
This is not easy though. On top of being notorious for ransomware, Microsoft is notorious for optimizing their solutions for lock-in, addiction if you will, which makes them incredibly difficult and costly to migrate away from. The benefits are immediate to those with the grit to migrate though.
But instead of highlighting any of this, the task farce appears to be operating under a false pretense that ransomware is somehow a platform-agnostic affair and that architecture is irrelevant while further ignoring the important role that architecture plays in preventing ransomware and neglecting to showcase Microsoft for being a common denominator that it is; bungling it massively if you will. This is so much the case that they only mentioned the word architecture once in their entire report. If anything, they appear to be adopting Microsoft’s “assume breach” approach which is just their way of shifting blame to the people who support and manage their unsupportable and unmanageable solutions. All of which forces me to question the degree of their expertise and their intentions.
As harsh as this may seem at first, questioning their expertise is fair when there seems to be no focus on preventative measures and devoid of even the most obvious architectural recommendations; no acknowledgment that most ransomware attacks are preventable, no acknowledgment that not all architectures are equal, and no acknowledgment that they often occur when fundamentals are abandoned or forbidden. More often than not, there’s an IT nerd saying, “I told you so.”, to their change-averse management post-mortem with emails to back it up and this just isn’t something that experts can simply ignore when trying to prevent ransomware.
Recommendations given, no response as expected.
To say the least, the IST report would look markedly different if boots on the ground were at least consulted with beforehand, hence why I began to question it so flagrantly as someone that has dealt with ransomware and its prevention for half a decade now. In an effort to clarify their expertise, I reached out to Katie Nickels, one of the task farce members, and she didn’t argue or lambast me with credentials proving otherwise and merely asked for my recommendations; a low-key admission of my expertise concern having merit if you’re into that whole social engineering thing.
Unsurprisingly and rather than supplying ransomware experts that could provide action items for people that actually work against ransomware on a daily basis which Microsoft has an abundance of, Microsoft instead supplied their digital diplomacy team comprised of Kemba Walden, Ginny Badanes, Kaja Ciglic, and Ping Look, which is curious because none of these people get wake-up calls when ransomware is dominating the infrastructure of their clientele. So far as I can tell, none of them seem to have even gone on the record about ransomware prior to this task farce being formed and it’s hard to see their role in the task farce and the absence of Microsoft’s complicity in their report as a coincidence.
When combining these oversights, the dominant presence of Microsoft spin artists within their task farce, and the high likelihood of a sizable donation from Microsoft to the Institute for Security and Technology though, none of this should come as a shock to you. As shown with fraud of dolphin-safe labeling/oversight, we live in a world where industry has a penchant for hijacking its own watchdogs with massive donations and further installing people throughout their ranks that are sympathetic to the plight of starving investors; all of which Microsoft has been accused of before which appears to be the case with the #ransomwaretaskforce. Roy Schestowitz refers to this approach as entryism and it may be time to pay more attention to these nefarious approaches in the tech space.
In summary, trying to cull ransomware via decree alone is only viable in comparison to throwing virgins into a volcano. Given Microsoft’s monopoly on ransomware attacks, the single best thing that any organization can do to prevent ransomware from ravaging your IT infrastructure is to migrate far, far away from Microsoft architecture entirely. Once that is accomplished, companies can implement multi-factor authentication, complex password requirements with password managers, and spare no expense on user training to further reduce their exposure to ransomware and other attacks that leverage these very same threat vectors. And companies can do this while reducing their ownership costs by a factor of 3 conservatively as showcased by IBM when they standardized on the Apple ecosystem; those less efficient at managing PCs at scale than IBM stand to see greater reductions.
You’re welcome to disagree and stay on Microsoft architecture or believe that approaching ransomware via bureaucracy- laden decrees is viable. It’s your funeral. But if you find yourself in this precarious position of deferring to lawyers and people that have never been on the hook to remove ransomware before, it may be a sign that you should do more reading and less talking about the matter instead. ⬆
The Web is a jungle and "open sites" (without restrictions or walls) are exposed to the 'feeding frenzy' of reckless plagiarists who call their "theft" something like "super intelligence" or "training"
If you keep calling people "paedophiles" when you yourself are connected to paedophiles (or are a paedophile), you're attracting a lot of unwanted attention to yourself