
Bonum Certa Men Certa

Taking Microsoft OOXML to Task

Any Windows/Office debuggers in the audience?

The following is a reproduction of a new post from Rex Ballard (I started this discussion thread), whose previous post we quoted the other day.


Message-ID: <31a66169-d9e7-4715-9e9e-e3488ebd36a9@25g2000hsx.googlegroups.com> From: Rex Ballard <rex.ballard@gmail.com> Newsgroups: comp.os.linux.advocacy Subject: Re: Leaked ISO Document Reveals Crooked ISO Amid MS OOXML Corruptions Date: Sat, 12 Jul 2008 08:20:23 -0700 (PDT)

[...]

ODF is a comprehensive document that provides detailed specifications from the high level document content down to the smallest elements of scalable vector graphics. There are some "standard" mime object types that are supported, such as PNG and JPEG, but other embedded formats must be installed using plug-ins which have to be authenticated by the user and by the system at installation time, and cannot be installed by the content. Furthermore, the installed content can easily be identified as trustworthy or not, and can be restricted in it's capabilities.

OpenXML on the other hand, is a high-level specification which describes the high level envelopes used to embed binary objects which are included in the content. The content itself contains the binary code which can call any function in any Microsoft library and has all permissions of the person opening the document. If a user account is set up as "Administrator", then the application can mess with the registry, create, download, and hide files, can execute applications in those files, can install any number of new viruses, and generally wreak havoc on the system.

I'll leave it to others to document the exact details (as I said, I'm busy these days), but I'm sure anyone who tries to publish these vulnerabilites will probably find themselves getting the same treatment that Tracy Reed of Ultraviolet.org got when he tried to publish his warnings about ActiveX controls back in 1997. Microsoft got a court injunction against him, and forced him to take down the content, claiming that it was being used to encourage hacking, and was damaging the Microsoft brand.

“I got a couple of docx documents and had trouble getting them to open, even with the plug-in for Office XP. Next thing I know, I get a notice from my registry auditor that I have 1300 new registry errors.”Over the last 10 years, we've seen these very same techniques, documented back in 1997, used widely to spread viruses including Melissa, Nimda, Sky, BugBear, and about 250,000 other viruses, worms, and malware, not including spy-ware and other "Microsoft Authorized" invasions of our privacy.

I got a couple of docx documents and had trouble getting them to open, even with the plug-in for Office XP. Next thing I know, I get a notice from my registry auditor that I have 1300 new registry errors. And suddenly, my PC is churning the disk-drive and the network connection at 3:00 AM (I'm getting old and have to get up), and the network shows that I'm uploading something at full speed, even though my computer is supposedly sleeping.

It isn't a back-up program that I'm running.

I would encourage COLA readers and OSS advocates to explore this in more detail.

get someone with Office 2007 to send you a docx file. unzip it using pkzip or winzip or unzip.

look at the binary files.

replace one binary object with another.

zip up the document,

see if your office-2007 user can read the "enhanced" document.

For those of you with OLE programming skills, create an OLE object that creates a file, and e-mails that file to you using smtp.

Send a document with this new ole object embedded (along with the others) and see if you get an e-mail.

I haven't tried this, and I don't know if it will work. I'm not sure how hard it would be to make it work. I just think it might be an interesting project worth investigating, especially if you are considering the migration of a few thousand users to Vista and Office 2007.

I'd love to see what the results turn out to be. After all, if it's that easy to take control of a recipient's machine just by sending them a "trusted" Word, Excel, or PowerPoint attachment, just think how much chaos a really aggressive malicious hacker, with a goal of obtaining marketable information about your business, could do.


Does ISO really want to approve such a 'virus'? As an international standard even? If someone tests the above, please post the outcome here or elsewhere. It would prove invaluable.

The last time a chain of ISO problems was cited, Ian Easson challenged an argument from Groklaw. He might wish read the following lengthy follow-up. ISO is in a deeper puddle of mud than before.

Brazil is a P member of SC 34, so according to my reading of the clause, it has the right to appeal if any of the three above issues apply, and arguably they all do. According to South Africa, if the issue is ISO's reputation, or if there is a matter of principle involved, Brazil can appeal. Even point three could apply, in that Brazil raises matters such as incorrect tabulation of votes, which, if true, one would hope ISO wasn't aware of.

[...]

Why did they bother to go, one might ask? Why vote, if votes disappear from the record? By my reading, Brazil paints a picture of an orchestrated event, tilted away from criticism or a negative result and a refusal to give substantive consideration to issues delegates wanted to discuss, due to time constraints Brazil calls arbitrary, and worse.

For details about the BRM in question, see [1, 2, 3, 4, 5, 6, 7, 8] and have your jaw sink to the floor. It was a bad plan from the get-go [1, 2, 3, 4, 5], but Emperor Microsoft was in a hurry and it even used its lobbyist Jan Van Den Beld to change the rules 'on the fly'.

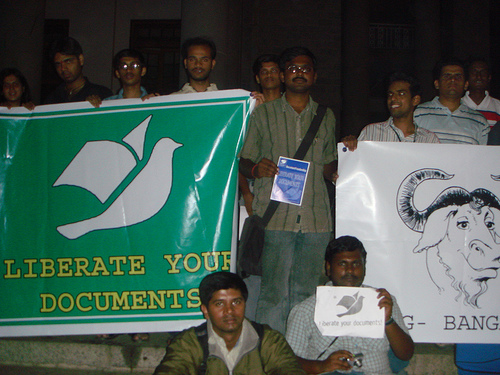
OOXML protests in India
From the Campaign for Document Freedom

Recent Techrights' Posts

43rd Anniversary of the GNU Project Announcement
Coming soon
SLAPP Censorship - Part 187 Out of 200: Reminding Ourselves of the Great Damage Garrett Did to Linux (for Microsoft)
he rejects freedom
 
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Thursday, September 17, 2026
IRC logs for Thursday, September 17, 2026
SLAPP Censorship - Part 188 Out of 200: Used, Then Discarded, by Microsoft (as We Predicted All Along, It's Always Like That)
The longer they carry on with it, the more scandalous this will get
Linux Kernel Becoming a Slopfest - Part 3 - Besieged by LLM Bots, Now Hiding Behind a Wall of JavaScript
The series began 3 days ago
Gemini Links 18/09/2026: Modern Linguistic, Boxing, Turning 40, and Solar MiniServer
Links for the day
Links 17/09/2026: Studio Closures and Negative Rumours About Microsoft XBox Again
Links for the day
What's Wrong with Microsoft's GitHub, New Article by Jacob Bachmeyer and Richard Stallman
licensed under a Creative Commons Attribution-NoDerivatives 4.0 International License
EBay is Going to Die Soon
Users will flee
Red Hat PIPs. The Only Question is, How Many?
Insiders know what's coming soon
This Week The Register MS Published a Page With "AI" 34 Times in It and It Was, as Usual, Paid SPAM!
Does The Register MS understand that it is doing harm to its audience (for temporary gains)?
General Assembly (Meeting of All Staff) Starts in Hour Ago to Discuss Strikes at Europe's Second-Largest Institution (EPO), Strikes to Last Until End of 2026 (If Not Further)
The media absolutely does not cover this and that's intentional
Cancel Culture is a Cancer That Harms Democracy, Justice, and Science. It's Designed to Help Corporations Vanish Their Critics.
"Codes of Conduct" sounds benign; in practice, however, it is not
Links 17/09/2026: Class Action Lawsuit Over GAFAM's "NameTag" and Automattic Hides What It Did to CEO Mullenweg (or Why)
Links for the day
Gemini Links 17/09/2026: Google Signals the End, ROOPHLOCH Coverage, EBay Uses Offensive Bots to Falsely Accuse Users of Stuff
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Wednesday, September 16, 2026
IRC logs for Wednesday, September 16, 2026
IBM's Anderon Another Opportunity for Debt-Loading, Publicity Stunts, Maybe Hidden Layoffs
Anderon is like Theranos
In Praise of 7 Years of Alex Oliva in the FSF, Not IBM
Thank you, Mr. Oliva, for 7 years of uncompressing advocacy and perseverance
SLAPP Censorship - Part 186 Out of 200: Love (Always Commands)
This coming Friday we celebrate our wedding anniversary
With Half of September Finished Clownflare Radar Sees GNU/Linux at 7% "Market Share"
On desktops/laptops
Linux Kernel Becoming a Slopfest - Part 2 - Bribes From Slop Pushers Divide Us
Money can and does divide people
Gemini Links 16/09/2026: Cards, Nature, and Conspiracy Theorists
Links for the day
Links 16/09/2026: Proprietary Chatbots Company Lets Humans Moderate Chatbots, "Putin Looking to See How Far he Can Push NATO"
Links for the day
The Only Still-Supported Version of Windows Breaks Itself (Again), the Microsoft Layoffs Will Carry on in Secret
In the US they marked about 7% for removal just this past summer
Wikileaks Turns 20 Just 18 Days From Now
it's fair to say they've endured online, but aren't lively/active
The Cyber Show Debunks the Alleged Intelligence in Slop
It's shorter than usual
Expecting Failure
Some things would not happen to technology (tech) experts because they know how things work and what to expect (or watch out for)
Links 16/09/2026: US Running Low/Out of Some Ammo Due to Wars, Slop Bots "Are Using an Outrageous Amount of Electricity"
Links for the day
"AI Slowdown" is Code Word for Bubble Imploding (Trying to Make This Slowdown Seem Wilful, an Act of Safety and Responsibility)
They help one another by inflating the bubble and making false excuses when expansion stalls
SLAPP Censorship - Part 185 Out of 200: What Reputation?
Helping monopolies and working for monopolies never made anybody popular
Gemini Links 16/09/2026: Slovenia, Catastrophe Ethics, and ROOPHLOCH 2026
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Tuesday, September 15, 2026
IRC logs for Tuesday, September 15, 2026