Video download link | md5sum e6992ceaa55d089f64f07013fd228f56
Microsoft Loves Linux FUD
Creative Commons Attribution-No Derivative Works 4.0
Summary: Today we wish to take stock of a bunch of misleading, sensationalist coverage about "Linux"; as usual, Microsoft is connected to that, even more directly than one might expect...
THE TECHNICAL sabotage by Microsoft is easily demonstrable, e.g. in Mesa and in Linux (the "contributions" by Microsoft are to Microsoft, not to Linux, and they promote proprietary surveillanceware, not Software Freedom). In the video above I discuss NTFS in Linux (indirect link to bypass sites we boycott).
"Nothing Microsoft does benefits anyone else,"Ryan said moments ago in IRC, "except for a few odd cases that were usually less than 100 lines anyway. Which someone else probably would have done regardless at some point..."
"They try to minimize the usefulness of their "Linux" work to anyone else, because they don't want to make "Linux" work better except in shackles under their Azure crap."
More importantly, however, so far this week I've seen many Linux-hostile headlines, usually in Microsoft-friendly and/or Microsoft-connected sites which have historically been Linux-hostile.
Ignoring
deliberate holes in Microsoft products, such sites would have you believe that Linux is the least secure thing on the entire planet!
As we put it in the latest batch of Daily Links, "while CISA admits Microsoft is full of holes that are
actively exploited Microsoft and its faithful media operatives try to shift attention to "Linux" [as we demonstrated a few days ago, linking directly to CISA's site]..."
So what on Earth is going on here? "Microsoft concern-trolling Linux while putting NSA back doors in Windows," to quote our editorial comment? Speaking of
actively exploited holes, two months after a patch had been made widely available we see
this article. "This was patched a very long time ago," we noted this morning, and "meanwhile, there are dozen of zero-day flaws in Windows that are remotely exploitable, not local privilege escalation..."
So it seems like there might be distraction going on. And maybe there's more to it than meets the eye...
Not only is it very hard for a malicious, unknown actor to actually leverage such a bug; it's also hard to prove that Microsoft manipulates the media
consciously in this case. We'd need to see leaked communications to actually prove such an assertion.
The net effect is the same and Microsoft staff now feeds the media with anti-Linux talking points. The stories are run by moles of the company, Microsoft-sympathetic 'gurus' who have moreover infiltrated the
Linux Foundation (an organisation that nowadays
ACTIVELY PARTICIPATES in such anti-Linux campaigns of semi-false talking points).
This keeps happening. We see it once in a few months, and this time it culminates in "old news" being
rerun (about a bug properly patched more than 50 days ago [
1,
2,
3,
4] and
before it was even known to the general public).
The real problem, according to CISA, is Microsoft. But CISA's "blog" almost never mentions "Microsoft". It just maintains a catalogue many Microsoft flaws.
"If there is a problem affecting non-Microsoft systems," an associate told us today, "then that is unusual and therefore news. If there is a remote exploit in the wild being actively exploited against Microsoft systems, that is the normal situation and thus not news."
Towards the end of the video I show
this new blog post from Debian's Russell Coker, noting that Microsoft gives the NSA
et al direct access to PCs, so no "security" measures from Microsoft should be taken seriously, to quote
the latest Daily Links.
To quote Ryan, who is a
former Microsoft MVP: "Local Privilege Escalations are bugs, yes, but they are of low concern (and do get fixed). Anyone with direct physical access to a computer can elevate their privileges eventually. And on Windows there's a ton of them which sometimes even bypass the TPM and Bitlocker. There was one in the print spooler, for example, last summer. But it happens all the time on Windows and you don't even see it much in "the news". Any user on the machine could become SYSTEM and read your files, even if they were "protected". So that's Windows for you."
bnchs noted that "in GNU/Linux, you would have to boot to another OS to get root."
Quoting Ryan some more: "Becoming SYSTEM is an even bigger disaster than becoming ADMINISTRATOR, because in Windows, this means that you're...well, part of the system. You can even patch and hook into things that are "secured" and off limits to ADMINISTRATOR. Stuff that normally requires digital signing no longer requires digital signing. So at this point, rootkit? Sure. And all it takes is someone running as a Guest or as a user with no administrator hat to run a file that knows where the vulnerabilities are. Microsoft was in the news (their news) recently for raising the bug bounty. It's still less than Google's, and way less than what those things are worth to nation state attackers, terrorists, and ransomware outfits. By a factor of $10,000:$1 sometimes."
MinceR said it's "still wasted money from their perspective [as] that could be better spent on corruption, ads and lawyers..."
Ryan continued: "Even if you get $40,000 out of Microsoft's bug bounty system somehow, the ransomware gangs can just exploit it and make $20 million or more on one hit. So they'll pay better each time and it's simply up to the conscience of whoever found the problem in Windows as to what they want to do with it at that point. So the bug bounties are a ruse, a smoke screen, and the illusion of responsibility. In Linux, people find and fix bugs all the time. The code isn't hidden. That leads, usually, to inevitable discovery, and quick patching."
"People want to find bugs in Linux and report and fix hundreds of the same type, so they develop tools that can do things like that. Microsoft is annoyed that you reported one. Even over a decade ago before profiling tools were not as robust, not by a long shot, Coverity Scan admitted that "open source software, in general" was less than half as buggy as a comparable proprietary program. The proprietary software is sort of like the worst case situation for your security because they have little incentive to fix it unless there's already malware out there and they just can't hide the bugs any longer."
"It's like General Motors [GM] putting defective ignition switches in millions of cars for a decade after they knew they were shutting off the car unexpectedly and killing people in accidents. GM figured it'll cost $1 a car to fix this problem, then come all of the recalls, and we'll just grind them down with stall tactics and lawyers and stuff if they ever find out, and the settlement will still cost less. So that's what we do."
⬆
Update: Since we made the video above a bunch of other Microsoft boosters (with history) joined this FUD campaign. Of course they don't mention what happened to Windows this past week (CISA reports). Left out from the video (3 examples) are:
And about half a dozen more. Screenshot below:
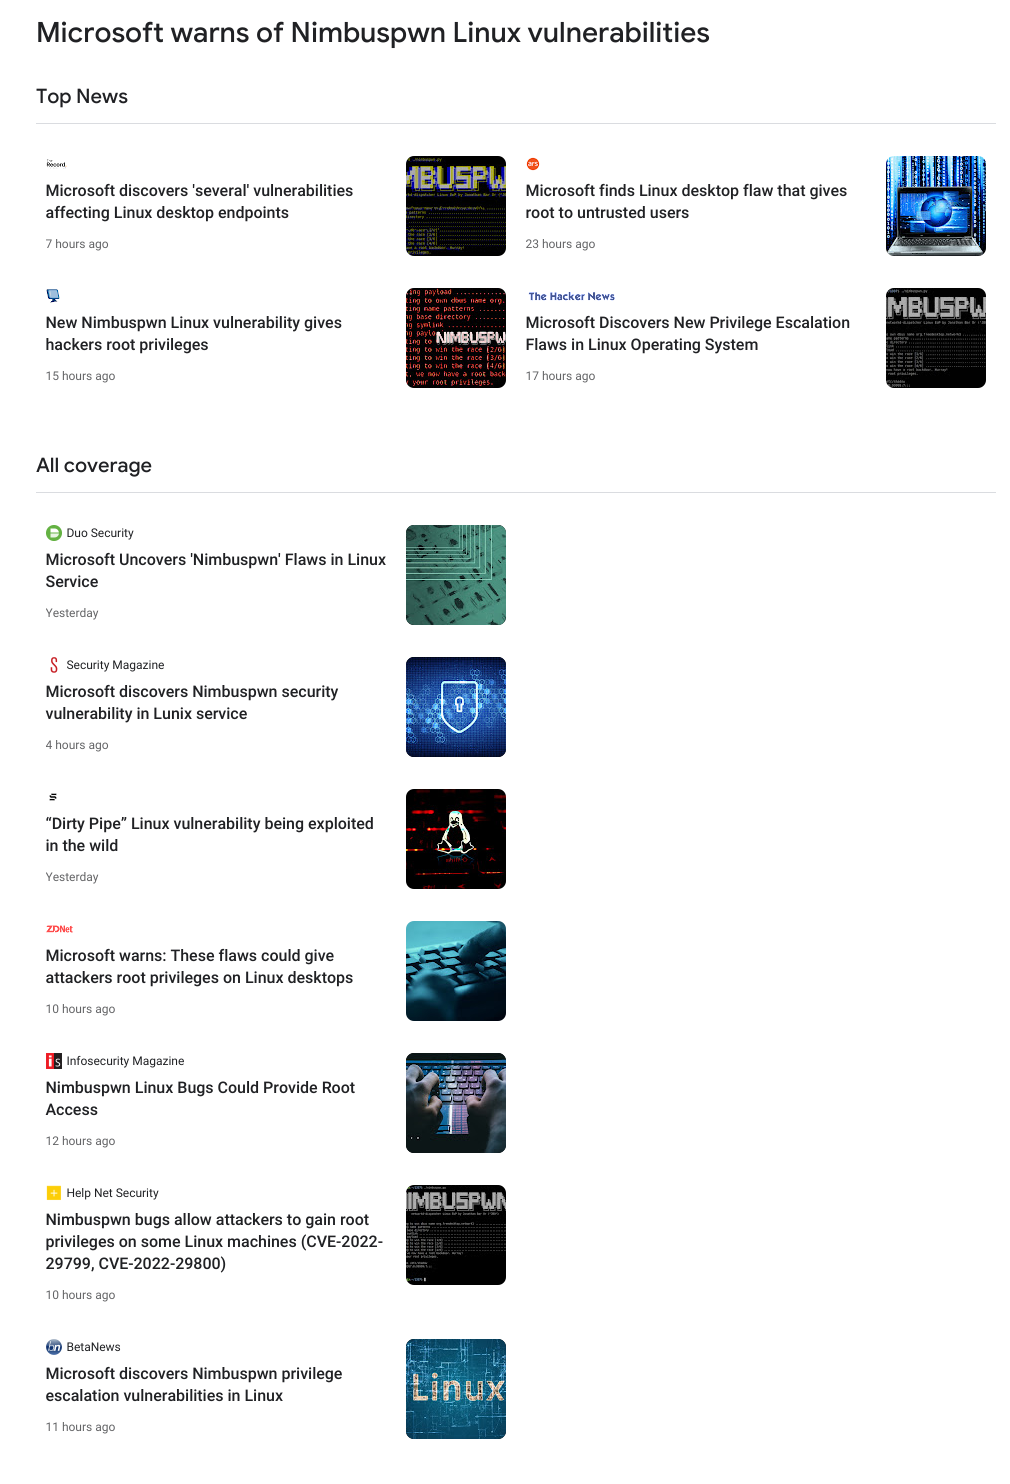
But yes, Microsoft loves Linux...
Microsoft loves Linux
FUD.

