Intercontinental Brigading - Part XXIII - What Garrett Did Puts Elections at Risk (Also in His Own Country, Where a Dictator Trusts Only Machines That 'Support' Him)
He's not even a "real" (patriotic) American as he presently holds three nationalities and his allegiance is to corporate money (he'd even squash his own spouse to get ahead or to spend time with a girlfriend while raiding the spouse's bank account after locking them up based on false pretexts and defamation).
Would you trust such a man with your computer security? A man whose own spouse accuses of rape? A man alleged to have broken legs (plural) of a puppy? UEFI 'security' is only as trustworthy as its ferocious boosters.
Previous Parts:
Democracy at Risk
Our Daily Links have long had a political section. That covers elections, among many other things. The Nation, for instance, reports that "Trump Just Told Us How He Intends to Steal the Midterms". Quoting the article:
The Alaska case is a red flag that Trump has no intention of accepting the results of an election that Republicans lose.
Imagine voting machines or election committees whose underlying systems are controlled by a dictatorship that loathes elections to the point of instigating violent insurrection. Imagine that dictatorship already has an ample history of selectively rejecting results of voting machines. Or calling Putin "humanitarian"...
Today we enter a subseries (series within series) about what "modern" voting machines would be subjected to if they all came with back doors. We'll run this subseries until the US election next week.
Suppose the dictatorship (or mere candidate) wanted complete control over computers, either of election staff or ballots. Suppose this dictatorship already enjoys a cozy relationship with Microsoft and generally tells Microsoft what to do.
Trying to Change the Subject
This is where "Restricted Boot" Garrett et al step in. Faithful servants of Microsoft's back doors (or bug doors), including BitLocker [1, 2], security does not interest them, they simply misuse that word. Garrett talks about "Restricted Boot" being broken right now, albeit nowhere in his own social control media. He's perfectly aware there's nothing worth defending; he wants to distract from what's happening. He hopes nobody will notice.
He always sought distractions and yesterday he commented on anything but "Restricted Boot" catastrophe. He spoke about trial costs; as noted last night, based on his own public statements and his spouse's public statements, he had already run out of money way before any judgement and it would be foolish to ignore such data points. He was borrowing already a year before an expensive trial, so it was clear that he - just like or along with his litigation partner from Microsoft - would pay nothing upon losing their cases. They were moreover based in another continent - very far away from London - so compelling them to pay anything would be a logistical nightmare, according to legal experts in the UK. They knew this. Politicians now understand this too and we need an elaborate reform to curtail such cross-Atlantic lawsuits - not only Russia is the culprit here.
"So the Solicitors Regulation Authority (SRA) is against mercenary solicitors and abusive litigation when it comes to Wagner," a reader has noted, "but is completely OK with it when it comes to Microsoft? What caused the SRA to pivot?"
We'll cover this some other time when we resume the SRA series (see Part I, Part II, Part III, Part IV].
Let's instead focus on the real issue - the one that caused Garrett to lawyer up (since 2021).
"Restricted Boot" Does Not verify Integrity, It Passes Control to Microsoft
"Restricted Boot" was never (genuinely) meant to be about security. As implemented, and as we saw last week, it's centralised and hence flawed by design. You can only trust it as much as you trust Microsoft.
Can you trust Microsoft?
Should you trust Microsoft?
Garrett can trust Microsoft because he was getting drunk with Microsofters. He was being paid to do the damage that he did.
"Restricted Boot" is Broken, Ample Evidence Exists That UEFI in General is Not Secure
Yesterday we shared about a dozen articles about this latest flaw.
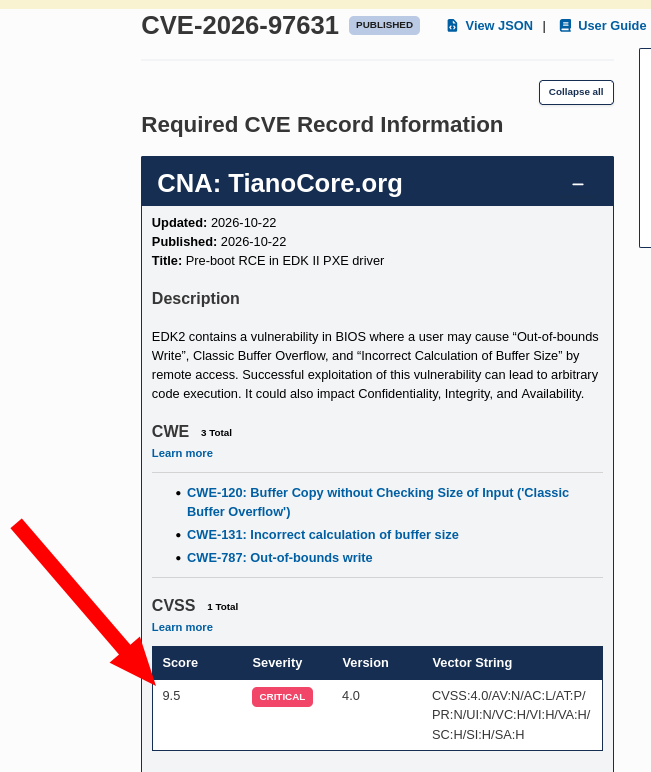
Severity 9.5 (out of 10).
This is severe enough to cause potential downtime and panic.
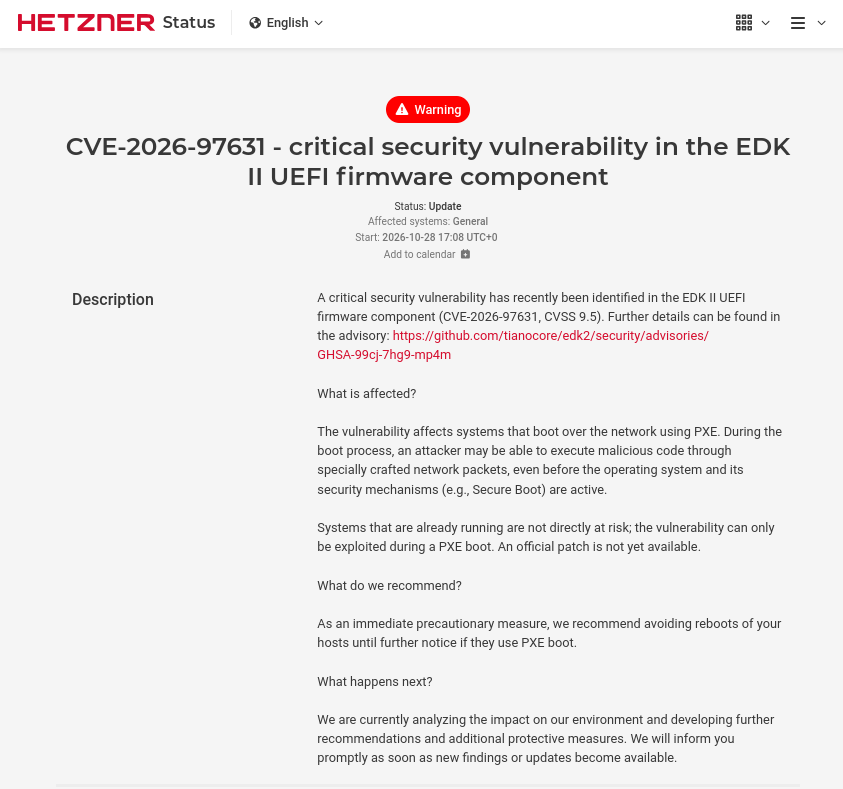
Imagine letting lots of servers rely on this bloated nonsense.
What would be the true ramifications when it comes to elections?
There are two main angles: 1) the dictatorship invalidates results, claiming that machines cannot be trusted (but selectively doing so); 2) the dictatorship breaks into machines to alter votes by tampering in stealth.
Either way, "Restricted Boot" does not accomplish what its boosters claim.
Heck, proponents of "Restricted Boot" aren't even security professionals [1, 2]. They try to compensate for it by name-dropping, e.g. "CIA" and "NSA" (pretending to be fluent in things they know very little about).
This isn't a matter of humour. People's lives and nations' democracies depend on autonomy.
With "Restricted Boot", autonomy gets taken away. It's a Microsoft remote control.
In the next few parts we'll look at the long history of cautionary tales and also 'name-drop' BootHole, Bootkit, and BlackLotus. █