Bonum Certa Men Certa

Never Ever Use Coprocessors for Cryptology, Especially If Implemented in the United States

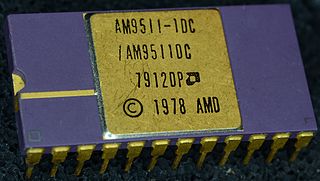
Can you read the source code in this microchip?

AMD microchip


Summary: Why the hype about "accelerated" cryptology (like polygons rendering, but for cryptographic purposes) is a dangerous trap that should be shunned and perpetually avoided

THE QUICKEST and most convenient way to undermine all encryption is to weaken random number generation, e.g. lower the entropy, making keys more predictable and thus easily crackable by supercomputers (or even standard computers). This is effective against everything, including online financial transactions, simply because it cracks the very core components of today's security: SSL, PGP, etc. My doctoral degree involved a great deal of work with entropy and my daytime job too sometimes involves it, so the subject is not foreign to me. I have been watching the NSA closely for a number of years, and always with great concern and suspicion. Now we know that the NSA compels (and even bribes) US companies to help undermine privacy, if not by direct handover of data (PRISM) then by making encryption too poor, setting up back doors, forcing companies to obey NSL/subpoenas, network wiretapping/DPI, or even a combination of all those things. No need for hypotheses anymore; there's plenty of hard proof now.


Intel, a cleverly-named criminal company (serving the intelligence community), whose hardware-level random number generator (hidden in silicon) FreeBSD refuses to trust (OpenBSD too is historically very critical of Intel) is no longer the only x86 player seeking to manufacture consent (blind trust) for encryption with no source code, just minuscule circuits of semiconductors. AMD, another US company, is now following suit with ardware-level cryptology (i.e. cryptic algorithms for cryptology, which is a non-starter). This is bad just because AMD is a US company (FreeBSD did not single out the US); any company from any country should not be trusted with this type of task. It's no better -- and it is probably much worse -- than proprietary software for one's security. To quote Michael Larabel's article about it: "Back in November was when patches first emerged for an AMD Cryptographic Coprocessor on Linux. This co-processor provides hardware encryption and other hashing functionality for the AES crypto API, AES CMAC, XTS-AES, and SHA cryptographic interfaces within the Linux kernel.

"Not much information is publicly known on this AMD Cryptographic Coprocessor but it's believed to be part of AMD's embedded ARM Cortex-A5 processor on upcoming server-class Opterons with TrustZone technology."

"Have we learned nothing at all from Snowden's explosive leaks?"So, Linux 3.14 will try to offload something so sensitive to proprietary code concealed in silicon. Bad idea. Very bad idea. Sure, it's Linux, but it does open itself to some blobs (e.g. Microsoft's hypervisor and more famously drivers for peripheral cards that handle graphics), firmware, and now peripheral, embedded-in-hardware proprietary algorithms. Have we learned nothing at all from Snowden's explosive leaks? Just look what Microsoft has done (total complicity with the NSA). A new poll at FOSS Force asks: "Do you think Red Hat is cooperating with the NSA by building back doors into RHEL?"

The responses may surprise you. Only 42% say "No". 28% say "I don't know" and 30% say "Yes". This relates to an article that alludes to Techrights. It was read by thousands and has been linked to by numerous news sites. I rarely ever comment in sites where identity cannot be verified (because of fakers), but this one challenged my claims and I had to respond. Here are my three replies:

It is not purely speculative. If you think that it is, then you must not have paid close enough attention.

I have been spending at least 2 hours per day since 2012 reading about the NSA. I knew what Snowden showed even before it was publicly known and I spoke about it with RMS on numerous occasions (he came to the UK to meet Assange and then myself, focusing on mass surveillance).

The truth of the matter just needs a little digging because the corporate press is not helping the general public find it out, just like it knowingly ‘buried’ a captured agent in Iran for several years (this leaked out in November).

Similarly, GNU/Linux sites did a very poor job covering (if at all) what happened in recent months regarding Linux. Let me summarise some facts (without links, as I don’t want to be put in the moderation queue again):

- Torvalds’ father said that the NSA had approached his son regarding back doors.

- Linux had a back door added to it about a decade ago. It got removed quickly afterwards and it wasn’t known who had added it. There was press coverage about it, but it was scarce.

- RSA received a bribe from the NSA to promote security standards with back doors.

- NIST and others had NSA moles and bogus (corrupt) peer review process to help usher in security standards with back doors.

- NSA is a large Red Hat client.

- The NSA sends patches to Red Hat, which in turn sends those for Linus Torvalds to put in Linux.

(the above two are now confirmed to me by Red Hat staff)

- BSD does not trust hardware-level random number generators, suspecting — quite rightly given the NSA’s track record — that it has too low an entropy.

- Several top-level Linux developers found vulnerabilities in Linux random number generation. They quietly (without much press coverage anywhere) addressed the issue (raising the entropy) a few months back. Only the latest kernel release has the fixes applied AFAIK (I don’t know if Greg K-H backported any of it because coverage is too scarce). To lay out the magnitude of this issue, it compromises SSL, PGP, etc. (pretty much everything with encryption, even passwords) not just at client side (desktop, tablet, smartphone) but also the server side (i.e. the Internet). This is huge! But the media hasn’t covered it.

Suffice to say, Red Hat has not done anything to convince me I was wrong. Instead, I notice that Red Hat staff is stalking me in LinkedIn and I see my article cited in several news sites which wrote about the issue in several languages (3 articles in Google News are in Spanish).

If you found holes in the above statements or if you want links attached, please request them and I will provide citations. I wrote about everything before, even years ago (NSA involvement in SLE* and RHEL I covered around 2007 or 2008).

I am frustrated to see people turning against the messenger rather than the message. I see a lot of the same done to Sam Varghese. We are making ourselves more vulnerable by refusing to listen to what seems uncomfortable.


Another reply:

I was thinking along the same lines — that Edward Snowden’s leaks (by the way, they’re not just his anymore, as anonymous people from the NSA reportedly leak more and more documents to be published under his name for their safety) can at some stage show encryption undermined at more levels (hardware level, or even kernel level). We already know that encryption was undermined at RSA and NIST by NSA moles, using bribes too. We also know that Linux (kernel) developers recently revised random number generators, after they had found a weakness.

Several state officials (in 6 state at the very least) now work to stop the NSA locally. Some call for a ban on companies that facilitate the NSA (that would include Red Hat), under the premise that they are complicit in crime. I am not kidding, watch the news this week (I don’t want to paste links here as the last time I did so my comment took half a day to appear).

Lastly, there are numerous E-mails sent from and to Red Hat. These further validated my suspicions.

I saw a lot of personal attacks (trying to discredit me or even remove links to my analyses). I even heard the usual personal attacks against Sam Varghese (which I expected from Red Hat because he dares to do real journalism, i.e. journalism that companies don’t like).

Trusting Red Hat should be based on its record, not emotional leanings and faith.

Don’t get me wrong. I was not offended by you and you oughtn’t be offended by my response. I am used to this type of divisive treatment (people trying to ostracise me) since the days I criticised Novell — only to be proven right throughout and at the very end (Novell gave its patents to Linux foes).

I hope you will wait patiently for more information and assess the facts based on their merit. Don’t rely purely/solely on what you read in OpenSource.com (Red Hat). I saw Novell doing its self-delusional spiel (IP “peace of mind”) and fortunately, at the end, Novell did not find enough fools to sell its lies to.

I have been frank in my analysis of Red Hat (on patents, build process, etc.) and if you want links for particular bits of my claims, just ask. I have a repository of tens of thousands of links I collect while researching. Sometimes people refuse to accept even a well-sourced claim because of cognitive dissonance — something I’ve had a lot of experience with when dealing with Microsoft spinners.

“Journalism is printing what someone else does not want printed: everything else is public relations.”

― George Orwell


Here is my original reply, challenging the counter-arguments:

This article starts with an incorrect assertion that I accuse “Red Hat of being in cahoots with the NSA.”

No, NSA is a big client of Red Hat (this was not just revealed but also confirmed to me by Red Hat staff some days ago, by E-mail) and it was also confirmed that NSA submits patches to Linux through Red Hat (think of NIST and RSA; we don’t even have NSA E-mail address to keep track of). Back doors can also be added outside the scope of source code, during a build process. My job involves dealing with this risk. I don’t think you read an essential earlier post:

http://techrights.org/2013/11/24/tpm-back-doors-patriot-act-etc/

This, in turn, links to proof that the NSA did try to put back doors in Linux, as noted by Torvalds the father. See:

http://techrights.org/2013/11/17/nils-torvalds-on-back-doors/ http://techrights.org/2013/09/20/linux-backdoor-question/ http://techrights.org/2013/09/25/surveillance-lawlessness/

Defending Red Hat makes sense, but mischaractering my position is a little unfair. I note that trusting Red Hat is not easy and based on articles I read half a decade ago, NSA was involved in the build process of Windows, OS X, SUSE, and Red Hat (only those 4 were mentioned).


The bottom line is this. Do not have blind trust in Linux. Not even access to source code is enough because the build process needs to be carefully checked and validated; moreover, Linux is joined with some proprietary code and even hardware-level code, so trust is seriously harmed. Now that we know about Red Hat's relationship with the NSA we should ask ourselves if the NSA is once again trying to put back doors in Linux, or worse, maybe it already did. Letting blobs enter the pipeline helps the NSA achieve (but hide) what it already said it wanted to achieve. ⬆

Recent Techrights' Posts

Intercontinental Brigading - Part XXXIV - Women as Hostages, Even Spouses
First he put his own spouse behind bars by accusing the spouse of what he himself seems guilty of
A Geminispace Tally
That's not the Web, it is an alternative to it
Intercontinental Brigading - Part XXXIII - Shooting the Messenger is a Presidential Tactic
why our ministers are looking for ways to fix the law.
"The Judge Accepted That Mrs Schestowitz Had Been the Subject of a Vicious Campaign of Online Harassment"
That's consistent with how they men treat women
Intercontinental Brigading - Part XXX - Breaking This Year’s Election Process With Bug Doors in Restricted Boot
Thankfully here in the UK we typically still vote with paper and pencil
 
Links 04/11/2026: "Democratic Establishment" Wins Big and "Pentagon Sued Over Hegseth’s New “Future of Warfare” Committee Led by Musk"
Links for the day
Andy's Latest Writings About Proton CEO Andy Yen, "JavaScript Required", and Slavery in Technology
Andy (of The Cyber Show) has some new material
Intercontinental Brigading - Part XXXII - Malfunctions Reported in Windows Voting Machines (as Usual)
"There are always problems," Ryan told us
Gemini Links 04/11/2026: GoAccess, Adopting Gopher, and Twisty Passages
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Tuesday, November 03, 2026
IRC logs for Tuesday, November 03, 2026
Intercontinental Brigading - Part XXXI - Microsoft and Promoters of "Secure Boot" Are to Blame
the important thing is that the dictator and Microsoft can remotely control all computers
Links 03/11/2026: Science Around "Near-Death Experiences" and "Do Animals Grieve?"
Links for the day
Gemini Links 03/11/2026: Guitar, 3D-Printable Electric Spinning Wheel, Against Haven Social, and More
Links for the day
Intel Corporation Down Over 51% in One Month, the US Bailout Didn't Work
Is the slop industry [sic] next?
Microsoft European Development Centre (EDC) Next to be Culled?
No time for that anymore
Mass Layoffs at SUSE, Over 10% of Staff Gone
Ignore their excuses
When You're a Software Developer and They Tell You That Your Occupation is Dead or Dying in Order to Sell Dysfunctional Offerings Based on Hype (and Plagiarism)
Disbelief is a strength when companies borrow trillions of dollars to sell a dud and construct a pyramid scheme
Links 03/11/2026: Slop-Tied Debt is Becoming a Crisis (Lenders Panic), "Ukrainian Journalists Urge Global Media Not to Look Away From Russian Aggression"
Links for the day
Malaysia Seems to be Exploring Digital Independence With GNU/Linux and More
not too bad
Microsoft Windows is Crashing in Republic of South Korea
Like in Japan, they seem to be shutting the lid on decades of Microsoft-isms
Think Less, Aim for Less (When It Comes to Hardware)
An abundance of hardware being wasted on a pyramid scheme will become a cautionary tale one day
Gemini Links 03/11/2026: Stargazing, Linux-Powered Prism "Ambient Computer", and Abandoning Streaming Disservices
Links for the day
GNU/Linux Made Big Strides in Portugal This Year
Microsoft had many layoffs in Portugal in recent years
GNU/Linux in Argentina Now Measured at 8% "Market Share"
Argentina is known for exporting skilled footballers, not advanced technology, but it has a large population, which we can hope will dump Windows
Microsoft is Borrowing Loads of Money While Telling 60,000 Workers to Take the "Offer" and Leave, Microsoft Wants Bailouts From the Dictator
Vote in elections and also vote with your wallet
Microsoft and Spoilt Food
Some whistleblowers may be needed here
Intercontinental Brigading - Part XXIX - Undermining US Election While Engaging in Lawfare in England (BBC) Against Publishers That Cover Anti-Election Violence
The elephant in the room is back doors in voting machines
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Monday, November 02, 2026
IRC logs for Monday, November 02, 2026
Links 02/11/2026: Bracing for US Election and New Zealand Has November 7 Election
Links for the day
Gemini Links 02/11/2026: Beginning With Gemini Protocol, Looking for CoCs, and Slop for Local Data
Links for the day
NDA-Compatible PIPs and RAs at IBM Red Hat
We welcome Red Hat whistleblowers who can share with us the NDA/s passed their way
The Tower of Babel
More is not better
When Large American "Tech" Companies Can No Longer Complete Payroll
In spite of several very large waves of Dell layoffs, which the media reported on, it seems like they are still experienceng payroll problems, maybe that's why money is being borrowed
GNU/Linux Rises in African's Largest Population
15% in Nigeria [...] A country with over 200 million people
The Register MS Has Just Published a Fake Article With "AI" 28 Times in the Page (Communist Party of China Entity Paid for That)
In IRC, someone has just pointed out that an article at The Register MS repeats Microsoft's lies about its financial situation
Windows Down to All-Time Low, Says statCounter, While Microsoft Tells 60,000 Workers They're No Longer Necessary
Microsoft must be feeling "salty" right now
A British Uphill Battle to Eliminate Microsoft and Its American Back Doors
There are places of work and homes where GNU/Linux is installed and regularly used, not as a mere hobby but as a hyper-productive, practical tool
Writing for Good
The Web has an abundance of junk
Technical Coverage of US Elections
When elections are done by computers and decided by computers it becomes a tech issue
By Killing the "Linux News Section" in Softpedia (the Most Popular Section, Based on Its Editor) Softpedia Killed Itself
Enjoy Ballmer
Linkspam in "It's FOSS" Today (and It's Not Even FOSS)
free-to-access ad for some dodgy companies and the URLs are 'tampered' for cashback
Links 02/11/2026: Slop Destroying Mathematics and "Democracy is Not on the Ballot" (in US)
Links for the day
Celebrating Photography, Celebrating Life, Celebrating Magnificent Humanity, Not Plagiarism Disservices
Any time we adopt or spread slop imagery we are participating in the problem
Year-Long Celebration Starts on Saturday
This coming Saturday we turn 20
Intercontinental Brigading - Part XXVIII - Microsoft Doesn't Want People to Speak About Microsoft-Controlled Restricted ('Secure') Boot, a Silent Injustice and Back Door/Kill Switch
Can we please stop treating this as normal or acceptable?
On Desktops/Laptops, Clownflare Sees Windows at Under 60% and GNU/Linux at 15% This Past Weekend
Impressive if accurate
Microsoft Lunduke is Slop
Microsoft Lunduke is just trying to stir up hatred
Intercontinental Brigading - Part XXVII - Shooting the Messengers (People Who Oppose Microsoft Back Doors), Even Across the Atlantic
Keep this in mind later this week when a dictator either discredits the voting or covertly tampers with the voting process
Microsoft Wants 60,000 Employees Gone (One Way or Another)
At IBM, 15% of staff got marked as candidates for removal; at Microsoft it's almost 30%
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Sunday, November 01, 2026
IRC logs for Sunday, November 01, 2026
Jean-Claude Van Linus
Claude talking?