Intercontinental Brigading - Part XXVII - Shooting the Messengers (People Who Oppose Microsoft Back Doors), Even Across the Atlantic
posted by Roy Schestowitz on Nov 02, 2026
Richard Stallman's writings about Restricted Boot, rightly rejecting it (Microsoft certificates controlling GNU/Linux), are still available online; I did audiocasts with him, discussing the matter 14 years ago
Previous Parts:
| 2026-10-12 |
Intercontinental Brigading - Part I - The Failed Attempt to 'Swat' Our Series About the Attacks and Crimes Committed Against Us |
| 2026-10-13 |
Intercontinental Brigading - Part II - An Outline of This Series |
| 2026-10-14 |
Intercontinental Brigading - Part III - Reporting Harassment From America to British Police |
| 2026-10-16 |
Intercontinental Brigading - Part IV - Harassment Registered With the Police Before Projection Attempts Made From America |
| 2026-10-16 |
Intercontinental Brigading - Part V - Keeping Linux Under Users' Control, Not Microsoft's (NSA) Control, Leads to Weaponisation of Cops (Killing the Messengers) |
| 2026-10-17 |
Intercontinental Brigading - Part VI - Racism Against Blacks |
| 2026-10-18 |
Intercontinental Brigading - Part VII - Weekend Abuse Reported to British Police (Rogue Actors Take No Breaks) |
| 2026-10-19 |
Intercontinental Brigading - Part VIII - How We Convinced British Police That the Americans Were Just Manipulating and Tricking Them at the Expense of British Taxpayers |
| 2026-10-20 |
Intercontinental Brigading - Part IX - Swatting is Not Funny, Swatting is a Murder Attempt |
| 2026-10-21 |
Intercontinental Brigading - Part X - American Back Doors Inside Our Computers, With Transatlantic Swatting Against Critics Thrown 'Into the Mix' |
| 2026-10-22 |
Intercontinental Brigading - Part XI - Losing Over a Million Pounds (Borrowed Money) to Try to Silence Critics of Restricted Boot With Microsoft-Controlled "Certificates" |
| 2026-10-23 |
Intercontinental Brigading - Part XII - Lawfare to Cover Up Microsoft's Restricted Boot Calamity (Microsoft as Authority Over Linux), Garrett Wants to Talk About Penises Instead |
| 2026-10-24 |
Intercontinental Brigading - Part XIII - Censorship by All Means Available in a Continent So Far Away, as 'Secure' (Restricted, Restriction by Microsoft) Boot Has a Crisis of Legitimacy |
| 2026-10-25 |
Intercontinental Brigading - Part XIV - Six Years of Learning Irish, But the Real Issue Was Microsoft-controlled 'Secure' (Restricted) Boot |
| 2026-10-26 |
Intercontinental Brigading - Part XV - Annualised Consequences for Opposing Microsoft Back Doors in Linux Since 2012 |
| 2026-10-26 |
Intercontinental Brigading - Part XVI - The Faustian Pact That Irritates Hired Guns is Still a Distraction From the Serious Harm Done by Their Clients to GNU/Linux Users (Notably Plagiarism and Back Doors) |
| 2026-10-27 |
Intercontinental Brigading - Part XVII - The Relevance of Silent Layoffs at Microsoft |
| 2026-10-27 |
Intercontinental Brigading - Part XVIII - Microsoft is Not the Victim (It Was Never the Victim), It's Just DARVO |
| 2026-10-28 |
Intercontinental Brigading - Part IX - Literature About Malignant Narcissists in America Silencing the Press |
| 2026-10-28 |
Intercontinental Brigading - Part XX - Restricted and Moot, or How 'Secure Boot' Turns Out to be a Disaster (Again) This Week |
| 2026-10-29 |
Intercontinental Brigading - Part XXI - Techrights Was Right, So Why Was It Punished by Lawfare While the Culprits Walk Away Scot-free? |
| 2026-10-29 |
Intercontinental Brigading - Part XXII - Still "Radio Silence" From "Restricted Boot" Perpetrators (After Techrights Proven Right Again) |
| 2026-10-30 |
Intercontinental Brigading - Part XXIII - What Garrett Did Puts Elections at Risk (Also in His Own Country, Where a Dictator Trusts Only Machines That 'Support' Him) |
| 2026-10-30 |
Intercontinental Brigading - Part XXIV - It's an Inherently American Issue and American Elections Are at Risk From Restricted ('Secure') Boot and LLM Chatbots (Disinformation at Scale) |
| 2026-10-31 |
Intercontinental Brigading - Part XXV - Election Integrity at a Time of Back Doors and Very Severe Bugs in UEFI |
| 2026-11-01 |
Intercontinental Brigading - Part XXVI - The "Law and Order" Candidate Who Crushes Both Law and Order and Even Rejects Election Outcomes (Insurrection Follows) |
Today, as promised, we move on to some of the 'meat' or the substance regarding back doors and their ramifications/consequences for election integrity everywhere. It impacts all nations that use electronic voting machines. In the US, their use is extensive and there's a dictator with a history of turning down election results - to the point of calling for violence, then attacking publishers (in another continent) that speak about it. He only accepts election results when he likes the results.
Last week there was press coverage about UEFI flaws dating back to the beginning (2010). Those are critical! It's not unprecedented either.
"Other recently discovered UEFI flaws include:
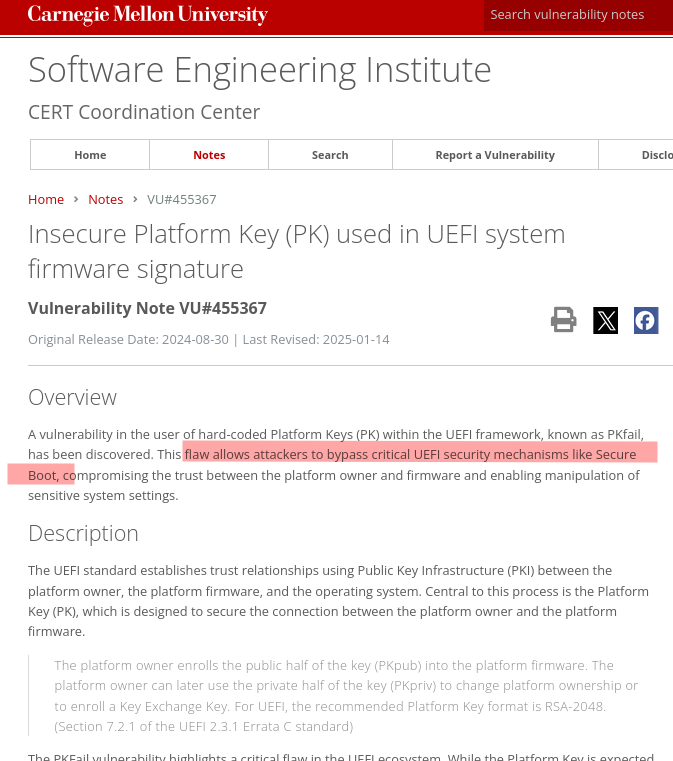
- PKFail, a supply-chain failure resulting from non-production test platform keys, public for more than a decade before they were discovered, used in hundreds of device models
- BootHole
- Bootkit and
- BlackLotus"
Those are just some of them (with buzzwords or labels attached/assigned to them). We've covered a lot more.
Consider this old report about PKFail (2024) and another old one from 4 years earlier.
This old one about "Bootkitty" is not about Linux but about UEFI.
These issues go deep. To quote: "UEFI-based Windows systems, and was followed with many other PoCs (EfiGuard, Boot Backdoor, UEFI-bootkit)."
There has been no lack of coverage [1, 2, 3].
Even the NSA took note:
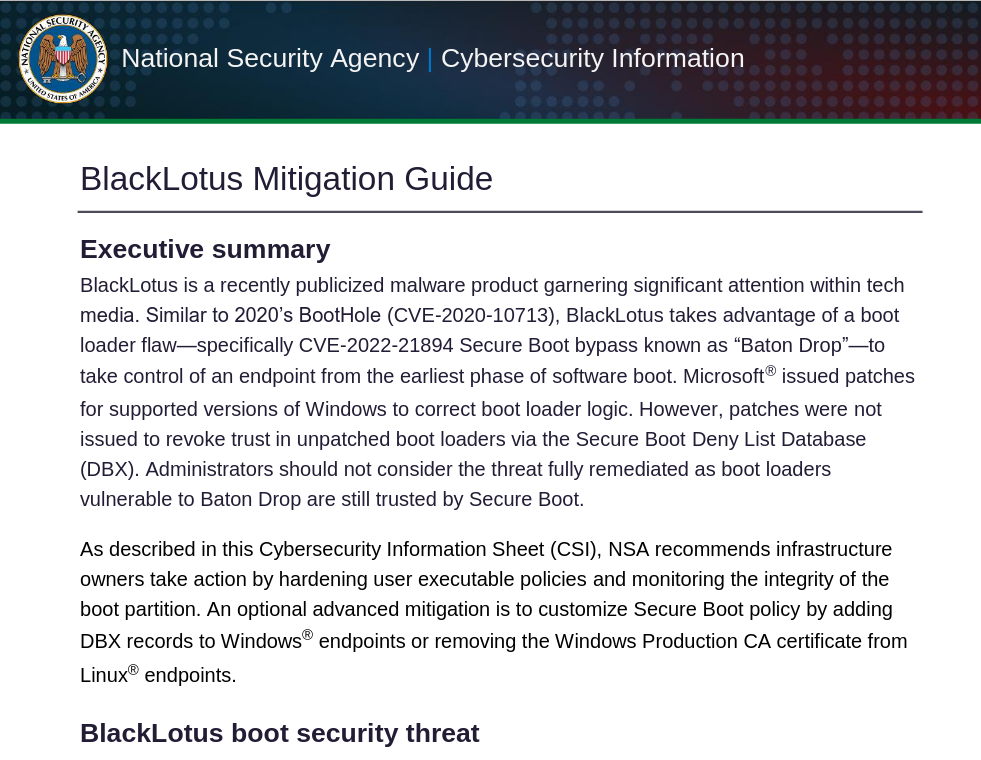
In 2025, regarding Restricted Boot: "ESET researchers discovered a new vulnerability, CVE-2024-7344, that allows actors to bypass UEFI Secure Boot on the majority of UEFI-based systems."
This was only a few months ago: "ESET researchers discovered 11 vulnerable UEFI shim bootloaders signed by Microsoft that allow attackers to bypass UEFI Secure Boot by exploiting decade-old vulnerabilities. UEFI shim bootloaders are tiny bits of code designed to bridge the gap between motherboard UEFI firmware and an operating system. The vulnerable shims, at versions 0.9 and below, can be used to bypass UEFI Secure Boot on any UEFI-based machine that trusts the Microsoft Corporation UEFI CA 2011 third-party UEFI certificate authority (CA) certificate, regardless of the installed operating system. Reported shims can be exploited to execute untrusted code during system boot, enabling attackers to deploy malicious UEFI bootkits even on systems with UEFI Secure Boot enabled. ESET reported findings to CERT/CC; the vulnerable UEFI applications were then revoked."
Those things also impact voting machines:
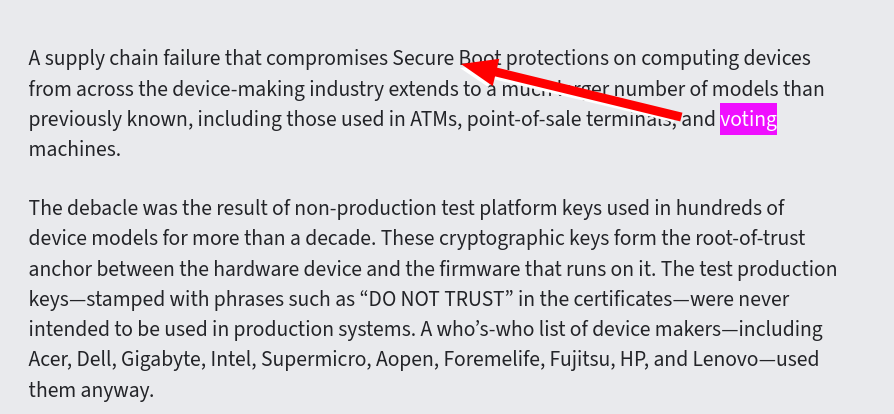
We have plenty of material there for a few days, regarding not just Restricted Boot being horrific but also giving a false sense of security whilst in fact giving Microsoft - a faithful servant of the dictator - back door access to every voting machine.
Not too long ago it was stated that a firm had "discovered 11 vulnerable UEFI shim bootloaders signed by Microsoft that allow attackers to bypass UEFI Secure Boot by exploiting decade-old vulnerabilities" and "UEFI shim bootloaders [are] vulnerable to Secure Boot bypass" (they're promoted by Microsoft staff that does not understand or pursue security).
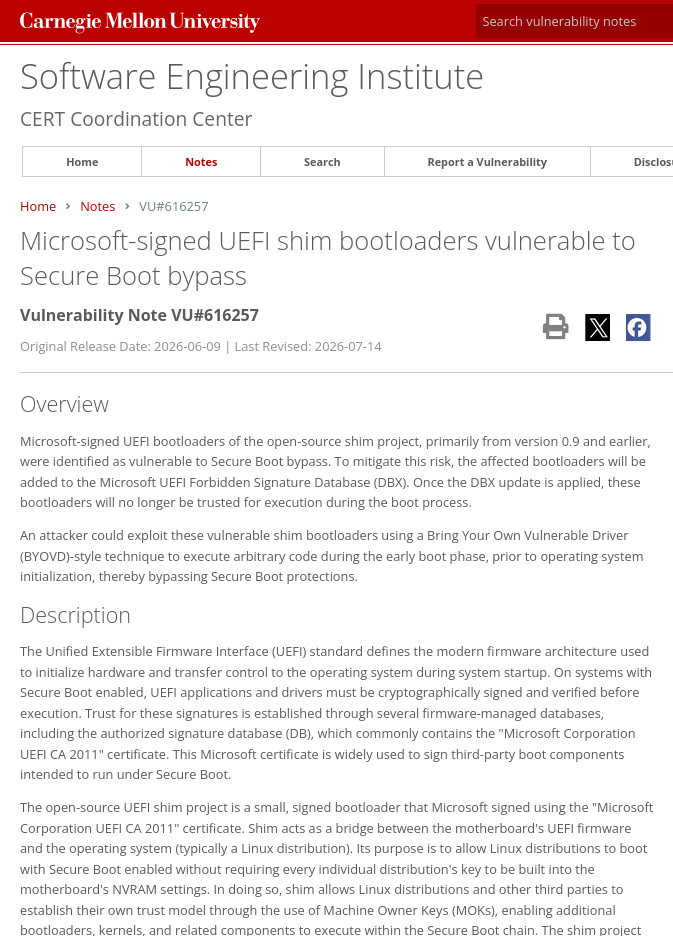
More snake-oil 'security' [1, 2]:
Keep this in mind later this week when a dictator either discredits the voting or covertly tampers with the voting process.
Apparently the problem is someone in the UK (and his wife!) because he has warned about this for 15 years. █