Bonum Certa Men Certa

The ISO Delusion: A Stack of Proprietary Junk (Slack) Failing Miserably

And the management that chose this junk resorts to blaming the victims

"Giving the Linus Torvalds Award to the Free Software Foundation is a bit like giving the Han Solo Award to the Rebel Alliance."

--Richard Stallman


Summary: When the company where I worked for nearly 12 years spoke of pragmatism it was merely making excuses to adopt proprietary software at the expense of already-working and functional Free software

LAST night we covered the use of Microsoft Skype in Sirius 'Open Source'. It only happened once, but that was enough to damage the brand and injure some workers' morale. Why would a company called "Open Source" something be eager to abandon Free/Open Source software, opting for proprietary stuff of the most vicious rival? What message does that send to longstanding clients or existing staff? What about potential/prospective/future clients and staff?


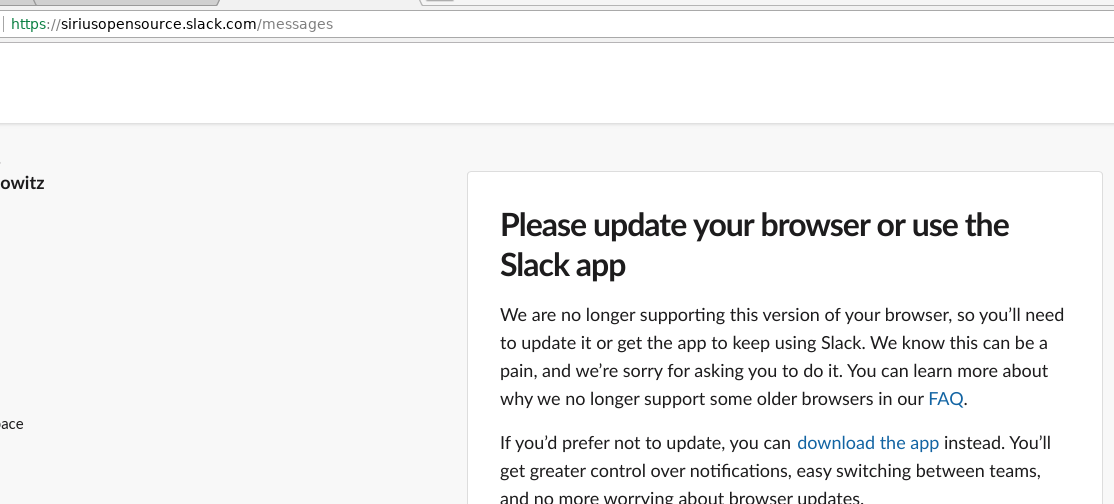
"Why would a company called "Open Source" something be eager to abandon Free/Open Source software, opting for proprietary stuff of the most vicious rival?"Slack on GNU/Linux is a mess. Slack on Free/libre browsers is almost an impossibility. So why on Earth would Sirius move away from Jabber and force/impose the use of Slack? I've uploaded 2 images from several years back; they're screenshots of what happened when I tried accessing Slack from a GNU/Linux PC using a decent Web browser that isn't controlled by spying firms:
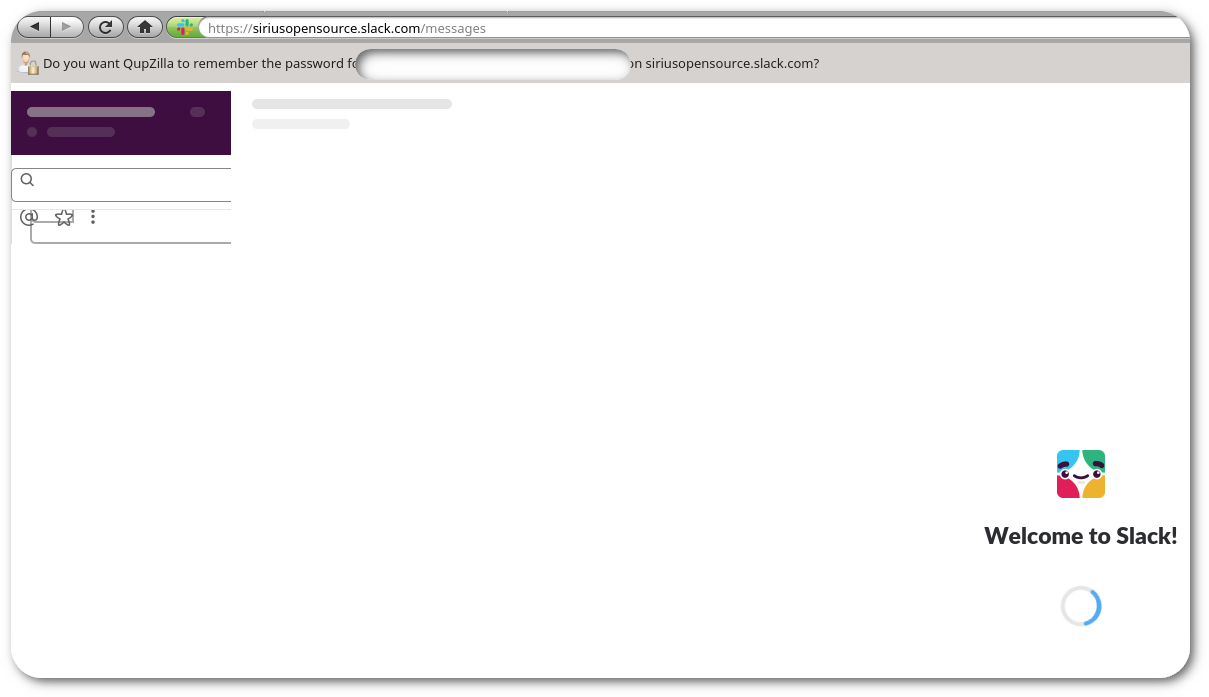
Slack on GNU/Linux PC


Broken Slack


That does not seem like it's going to work, does it? This is from 2019. It has only gotten worse since.

So we've just belatedly used two screenshots of what Slack looks like on GNU/Linux with a proper (Free/libre) browser; "bossware" that insists on browsers which spy on their users. Using some User Agent (UA) sniffing they try to undermine or prevent access with perfectly capable browsers (if the UA is faked, there's a way to get in).

Back then I wrote to an incompetent manager who threatened me repeatedly for not using Slack: "I tried to access my account from two computers, from two browsers, including Chrome. It's not working. See screenshots. It only works from Rianne's laptop."

At one point they agrees to let me use Rianne's laptop, but then they "changed their minds" (in other words, they had lied to me right to my face in the illegal contract-signing). I got this:

xxxx wrote on 21/07/2019 02:23: > Hi Roy, > > You need to fix this problem and use Slack. > > You are a well qualified tech who can fix this issue and comply with > management’s request. > > As I have explicitly explained to you that you need to have your log in > for Slack and not use Rianne’s. Yet today you’re logged in via Rianne’s > and not using yours even though you sent me details of your own log in. > > To refresh your memory, this is from my previous email.

I need to install a new OS or a new browser for this.


Remember that the company never even paid us for any of our hardware purchases (for our work machines). That seems unreasonable.

"Slack itself has been having issues and it was sold to Salesforce."In hindsight, it seems clear this manager scared away almost all the technical people. The damage was irreversible.

Slack itself has been having issues and it was sold to Salesforce. The New York Times reported Salesforce layoffs earlier this month. The Wall Street Journal published this article noting that Slack just made bloated proprietary junk nobody truly wants to depend on:

When Salesforce Inc. bought the messaging application Slack for $27.7 billion almost two years ago, it said the marriage would “transform the way everyone works in the all-digital, work-from-anywhere world.” Corporate technology buyers so far aren’t impressed, analysts said.

The acquisition sought to capture the fast-growing market for communications and collaboration software during the Covid-19 pandemic, as employers sent workers home and shifted to remote systems.

Today, companies in the market for customer-relationship management software — Salesforce’s signature product — don’t appear to be swayed one way or another by the addition of messaging and collaboration features, said Liz Herbert, a vice president and principal analyst at information-technology research firm Forrester Research Inc.

“We don’t really see, when it comes to Slack, any pent up demand from Salesforce’s base for a tool like that,” Ms. Herbert said. “It really hasn’t become something compelling,” she said.


Salesforce bought itself a dud and in December of last year the CEO said that he would leave this month.

From what we can gather, the decision to adopt Slack came from the CEO, who posted Trump support tweets while encouraging staff to use pictures of superheroes in Slack. How childish and unprofessional. What a betrayal of Free software. Is this really the same person who became a patron of the Free Software Foundation? Maybe his personal life took him on a crazy ride -- a subject we might revisit some other day in another month.

To be clear, Slack doesn't do anything that Free software cannot do. It's bloated and it is not secure. It also has security breaches.

Just two days before the above E-mail message (from a manager) I received this:

-------- Forwarded Message -------- Subject: 💥 Slack Security Incident Date: Fri, 19 Jul 2019 16:58:59 +0000 From: Keybase <notify@keybase.io> To: r@schestowitz.com

*schestowitz*,

We've been getting questions about this, so an announcement for everyone.

Today, Slack announced that a break-in from 2015 was possibly more severe than previously announced. A lot of people have been getting emails today. It seems 1% of Slack users still had compromised accounts (after 4 years); but more seriously, Slack has not disclosed what percent of Slack teams had their messages stolen. Also, if a small fraction of users have had compromised accounts, that may still mean a majority of teams were compromised.

We're sending this note because people are now asking if this could happen with Keybase teams. Simple answer: no. While Keybase now has all the important features of Slack, it has the only protection against server break-ins: *end-to-end encryption*.

Keybase's CEO, Max, just wrote how this Slack incident personally affected him *in a new blog post* <https://keybase.io/blog/slack-incident>.

tl;dr. Hackers who break into Keybase's servers could not read your company's, family's, friend's, or community's messages. Hope this simple update answers everyone's questions.

*https://keybase.io/app*

And Keybase is free! ❤️ the Keybase team


Slack took over Keybase and Slack itself was a vulnerable piece of garbage with habitual data breaches. The Keybase reputation was tarnished and not many people seem to be using it anymore, certainly not me.

I eventually responded to the manager as follows:

> Hi Roy, > > You need to fix this problem and use Slack. > > You are a well qualified tech who can fix this issue and comply with > management’s request. > > As I have explicitly explained to you that you need to have your log in > for Slack and not use Rianne’s. Yet today you’re logged in via Rianne’s > and not using yours even though you sent me details of your own log in. > > To refresh your memory, this is from my previous email.

I'm going to try to install another browser, as Chome and other browsers don't work for me. They don't show anything when I log in (I sent you screenshots). Maybe I'll be logged in with my username in a few hours when it's installed (if that works).

In the meantime, I have to raise other concerns.

The inevitable has happened to Slack. They announced it days and and they can be held criminally accountable

To say that Slack got merely “compromised” would be an understatement Yes, it did in fact get compromised, but it’s a lot worse. It’s far worse than a compromise per se. I'm going to explain, starting with the basics.

Slack accumulates all data and never deletes any of it. GDPR should be applicable here and I suspect that EU authorities have not assessed that aspect just yet. What Slack is to users isn’t what it is to Slack, the company. The Electronic Frontier Foundation (EFF) issued strongly-worded warnings about Slack and even Microsoft utright banned Slack for security reasons. They very much foresaw the latest disaster. It’s difficult to assess or measure because it’s almost impossible to track the sources of rogue actors’ data.

Slack did not have a mere ‘incident’. They knew about it for quite some time (at higher levels, too). It’s the complete doomsday scenario, an equivalent of having one’s own Jabber server completely and totally hijacked, and all communications in it (names, passwords) stolen. But in the case of Slack millions of businesses are affected. In one fell swoop. Just like that. Even the public sector. Military, hospitals, you name it…

Slack got cracked, but they won’t admit that. They will lie about the extent of the damage, just like Yahoo and Equifax did (each time waiting months before revealing it was orders of magnitude worse). They game the news cycle that way. People must assume that all data is compromised. Businesses and their clients’ data is on Slack. Even HR stuff, which gets passed around in internal communications. Super-sensitive things like passwords, passports and so on.

Who was Slack data copied by? Mirrored or ‘stolen’, to put it another way? Possibly by rogue military actors that can leverage it for espionage and blackmail, as many do. Covertly. You rarely hear about blackmail because that’s just the nature of the blackmail. It happens silently. Some would say Slack got “hacked” (they typically mean cracked). But it’s actually a lot worse than getting cracked! I'll explain further…

About a month ago Slack got to its IPO milestone. But it committed an actual crime by not informing the customers of the breach. They would change passwords etc. had they known. But Slack did not obey the law. It did not inform customers. It announced all this after the IPO, in order to make shareholders liable, and it did so late on a Friday (to minimise press coverage about this likely crime). The shareholders too should sue for concealment of critical information.

Slack knew what had happened and why it waited all this time. This scandal can unfold for quite some time to come.

It would be wise to move to locally-hosted FOSS. However, that would not in any way undo the damage of having uploaded piles of corporate data to Slack and their compromised servers. In the coming days many companies will come to realise that for years they tactlessly and irresponsibly gave piles of personal/corporate data to Slack and now a bunch of crackers around the world have this data.

You can expect Slack to stonewall for a while, saying that it’s the weekend anyway. When it comes to Slack, expect what happened with Yahoo; First they say it’s a small incident; Months pass; Then they toss out a note to say it was actually big; A year later (when it’s “old news”): 3 BILLION accounts affected.

Now, like Yahoo, they will downplay scope of impact. A lot of companies can suffer for years to come (e.g. data breaches, identity theft).

I have great concern for the company where I'm working for almost a decade, including our compliance with the law and our clients' compliance with the law. This is why I bring this up.

I'm going to install something new and see if I can somehow logged in. I already tried, unsuccessfully, from two of my laptops.


In summary, Slack is a pile of garbage. With Slack, Sirius too became a pile of garbage. They deserve each other.

A few weeks ago John Goerzen wrote: "I loaded up this title with buzzwords. The basic idea is that IM systems shouldn’t have to only use the Internet."

Slack does not work when the company has downtime. It happened several times, which meant people could not speak to colleagues for hours. Why was our Jabber server shut down? Surveillance through Slack?

Remember that Sirius kept promoting fake security as if the company is a bunch of people who never used computers before. When clients ask about ISO certification (not an isolated incident) they don't seem to understand what truly happens inside Sirus. There's spying, outsourcing, security breaches and so on. Someone needs to talk about this. ⬆

Recent Techrights' Posts

Links 04/11/2026: Slop Helps Break Laws and Scam Altman Pretends Chatbots Are Persons
Links for the day
Intercontinental Brigading - Part XXXVII - Tasteless, Tactless Time for "Virtue-Signalling" (When Your Actions Are Much Like the GOP's)
Violence by cops isn't a "leftist" thing
United Arab Emirates: GNU/Linux at Over 8%
According to statCounter
As XBox Goes Out of Business Helen Chiang Adds Insult to Injury
XBox sales are worst in 25 years
Intercontinental Brigading - Part XXXIV - Women as Hostages, Even Spouses
First he put his own spouse behind bars by accusing the spouse of what he himself seems guilty of
 
Intercontinental Brigading - Part XXXIX - Crime Numbers Regarding GGG (Americans) and Why Those Still Matter
Time does not undo the actions
Intercontinental Brigading - Part XXXVIII - Telling the Police About the Defamatory Blog Where Posts Targeted My Wife and I (From Across the Atlantic Ocean)
Two years ago we spoke to cops a lot
The Register MS is Losing Money Again, Based on The Register MS
Selling out didn't pay off for very long
There Are No "Layoffs" Anymore, Layoffs Got Rebranded
We're entering bizarre times when layoffs are said to be "down" (according to the regime that suffered a 'bloodbath' in the election) because companies quit using the term "layoffs"
Gemini Links 05/11/2026: Rivers of London, Soul Cakes, STMicroelectronics, and Slop
Links for the day
The Register MS Has Just Published Fake Article With "AI" 84 Times in the Page Because It Was Paid to Do This!
Astounding number of mentions of "AI" (84 in total)
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Wednesday, November 04, 2026
IRC logs for Wednesday, November 04, 2026
Gemini Links 04/11/2026: Abacus and Spare IT Equipment
Links for the day
Viet Nam and Thailand at High Adoption Levels of GNU/Linux, Other Nations Nearby Are No Exception
Helen Chiang and her colleagues say it's a "clown show" at Microsoft
Richard Stallman on What It's Like to be Threatened by Strangers With Software Patents
We hope that some EPO insiders will take time to listen to this talk
Stealth Layoffs at IBM (PIPs and Bailouts)
string of reports or unverified hearsay
Steven Vaughan-Nichols is Slop
Just look at this
The Register MS is "Hosting a Dinner" for Sponsors
Remember that The Register MS keeps publishing spam about "AI"
Intercontinental Brigading - Part XXXVI - A Potent Microsoft Threat to Administration of Justice Globally (Not Just Fair Elections)
Breaking into machines to cover up one's own crimes
Intercontinental Brigading - Part XXXV - When One Does Not Understand Security (Nor Ever Pursues Security)
One might therefore conclude that Garrett is a proponent of American back doors
Links 04/11/2026: "Democratic Establishment" Wins Big and "Pentagon Sued Over Hegseth’s New “Future of Warfare” Committee Led by Musk"
Links for the day
A Geminispace Tally
That's not the Web, it is an alternative to it
Intercontinental Brigading - Part XXXIII - Shooting the Messenger is a Presidential Tactic
why our ministers are looking for ways to fix the law.
Andy's Latest Writings About Proton CEO Andy Yen, "JavaScript Required", and Slavery in Technology
Andy (of The Cyber Show) has some new material
Intercontinental Brigading - Part XXXII - Malfunctions Reported in Windows Voting Machines (as Usual)
"There are always problems," Ryan told us
Gemini Links 04/11/2026: GoAccess, Adopting Gopher, and Twisty Passages
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Tuesday, November 03, 2026
IRC logs for Tuesday, November 03, 2026
"The Judge Accepted That Mrs Schestowitz Had Been the Subject of a Vicious Campaign of Online Harassment"
That's consistent with how they men treat women
Intercontinental Brigading - Part XXXI - Microsoft and Promoters of "Secure Boot" Are to Blame
the important thing is that the dictator and Microsoft can remotely control all computers
Links 03/11/2026: Science Around "Near-Death Experiences" and "Do Animals Grieve?"
Links for the day
Gemini Links 03/11/2026: Guitar, 3D-Printable Electric Spinning Wheel, Against Haven Social, and More
Links for the day
Intel Corporation Down Over 51% in One Month, the US Bailout Didn't Work
Is the slop industry [sic] next?
Microsoft European Development Centre (EDC) Next to be Culled?
No time for that anymore
Intercontinental Brigading - Part XXX - Breaking This Year’s Election Process With Bug Doors in Restricted Boot
Thankfully here in the UK we typically still vote with paper and pencil
Mass Layoffs at SUSE, Over 10% of Staff Gone
Ignore their excuses
When You're a Software Developer and They Tell You That Your Occupation is Dead or Dying in Order to Sell Dysfunctional Offerings Based on Hype (and Plagiarism)
Disbelief is a strength when companies borrow trillions of dollars to sell a dud and construct a pyramid scheme
Links 03/11/2026: Slop-Tied Debt is Becoming a Crisis (Lenders Panic), "Ukrainian Journalists Urge Global Media Not to Look Away From Russian Aggression"
Links for the day
Malaysia Seems to be Exploring Digital Independence With GNU/Linux and More
not too bad
Microsoft Windows is Crashing in Republic of South Korea
Like in Japan, they seem to be shutting the lid on decades of Microsoft-isms
Think Less, Aim for Less (When It Comes to Hardware)
An abundance of hardware being wasted on a pyramid scheme will become a cautionary tale one day
Gemini Links 03/11/2026: Stargazing, Linux-Powered Prism "Ambient Computer", and Abandoning Streaming Disservices
Links for the day
GNU/Linux Made Big Strides in Portugal This Year
Microsoft had many layoffs in Portugal in recent years
GNU/Linux in Argentina Now Measured at 8% "Market Share"
Argentina is known for exporting skilled footballers, not advanced technology, but it has a large population, which we can hope will dump Windows
Microsoft is Borrowing Loads of Money While Telling 60,000 Workers to Take the "Offer" and Leave, Microsoft Wants Bailouts From the Dictator
Vote in elections and also vote with your wallet
Microsoft and Spoilt Food
Some whistleblowers may be needed here
Intercontinental Brigading - Part XXIX - Undermining US Election While Engaging in Lawfare in England (BBC) Against Publishers That Cover Anti-Election Violence
The elephant in the room is back doors in voting machines
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Monday, November 02, 2026
IRC logs for Monday, November 02, 2026