
Bonum Certa Men Certa

EPO Breaking the Law With Microsoft and Promoting Fake 'Encryption' That Violates Confidentiality on Many Levels

Video download link


Summary: An explanation of how truly ridiculous the EPO has become, handing over to Microsoft (and to the US government) just about all of the EPO's communications in direct violation of the law, as well, so the only question now is, will the law actually be enforced soon? Contact your local MP/MEP and report this to him/her.

THE EPO is breaking the law. The António Campinos regime is just as bad as Benoît Battistelli's, even when it comes to privacy and pressuring judges to allow unlawful patents, such as software patents.
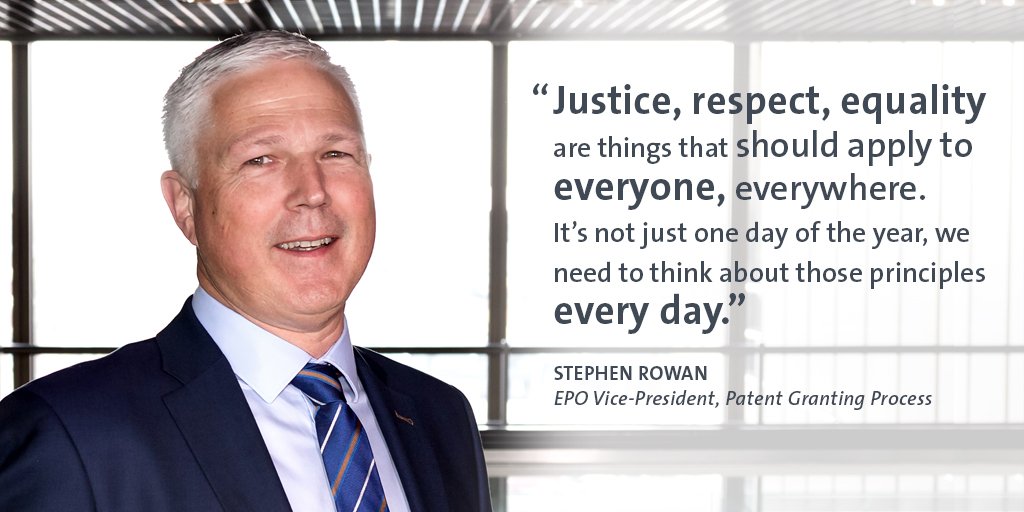


Steve Rowan - Vice President DG1 - Patent Granting ProcessIn parts of the series prior to this one, including Part II, we explained what the EPO had done and why it's illegal. I recorded a video (the one above) prior to the publication of Part II.

It's a long video, we could add a lot of links to it (I thought of many that would be relevant while recording it, but failed to take notes throughout), though the ones that seem of most relevance are Microsoft and the NSA relations, the latest Exchange fiasco (as recently as hours ago they still try to distract from it), how end-to-end encryption (e2ee) really works and some background about Stephen Rowan. The full text of the communication is reproduced below:

04.02.2021

Home > Organisation > DG 1 > The Vice-President > Announcements > 2021

Outlook Migration to the Cloud


Data encryption requirements for sending highly confidential data via Outlook

As announced in previous intranet items published in May and December 2020, our Outlook mailboxes are being transferred to the cloud. The transfer will take place in phases and cover only emails since 1 January 2021. As regards the patent grant process, only the following documents are classed as "EPO strictly confidential" and must not be sent by email without encryption: (i) application documents of unpublished applications (EP, PCT, national) (ii) search reports, search opinions, communications and decisions relating to unpublished applications (iii) search statements resulting in the disclosure of unpublished application documents (Guidelines B-III, 2.4; B-IV, 2.4) (iv) documents excluded from file inspection (documents which are marked as non-public in DI+, such as dissenting opinions, medical certificates, PACE requests, etc.) Guidance for the storage of strictly confidential information in the cloud The storage of strictly confidential documents in the cloud should be avoided, and data should not be copied unnecessarily from the EPO's specialised document management systems such as DI+. In practice, this means that, instead of e.g. copying data into an email, you should send a link to the document in the document management system (see also "How to send an email with document links or zipped attachment via Outlook"). Where sharing of strictly confidential data is necessary, the data must be encrypted before storing it in the cloud or sending a link to it via email. It is strongly recommended that you do not send the data directly in an email but instead encrypt the document, store it in the cloud, e.g. on SharePoint or OneDrive, and then send the recipients a link to the encrypted document by email. The password then needs to be shared via a separate channel, e.g. in a Teams chat, via Skype or on the telephone. Sending encrypted attachments is strongly discouraged, as they might not pass spam filters: using encrypted attachments is a very common way to infect user computers, so our email gateways do not allow encrypted attachments to be sent from or to our Outlook cloud instance. The easiest and safest way of encrypting a document is to use the built-in capabilities of the Office programs. Simply protect the document with a password, which also will encrypt the document with a strong encryption algorithm. Obviously, this password should be safe. As a rule of thumb, it should be about as complex as our login passwords, but of course not identical to a password already used. Chat is a good way to send the password, as a long random password can be easily copied and pasted from the chat into the password prompt in the Office program. Examples of how to apply encryption in popular Office programs are in the document annexed here.

Reasons and background

The level of security provided by Microsoft's cloud services is very high and will even mean an improvement in information security for our email system. In the cloud, our mailboxes will be protected by the most sophisticated systems. Email in Microsoft's datacentres is stored with a high standard of encryption, both in transit and at rest. With the help of contract terms, a data protection agreement and technical implementation, the EPO has ensured the best possible protection for the data stored using Microsoft's cloud services. Microsoft guarantees that the data itself is stored on EU servers within the jurisdiction of the European data protection rules (GDPR). Under the US Foreign Intelligence and Surveillance Act (FISA) and the US Clarifying Lawful Overseas Use of Data Act (CLOUD Act), Microsoft is obliged to grant security and intelligence agencies access to data stored in its cloud, even when stored on EU servers. However, the protection level offered by Microsoft is still sufficiently high for DG 1 processes in place for confidential data exchange not to need encryption. By contrast, to comply with the highest standards, which of course include the requirements imposed under the GDPR, encryption is needed for strictly confidential data. The guidance on the use of cloud tools therefore states that it is only strictly confidential data that must not be stored in plain form in the cloud, whereas merely confidential information can be stored there without limitations. The EPO defines "strictly confidential" in its "policy for information classification" (document attached) as: EPO strictly confidential: Information unauthorised disclosure of which could compromise or cause severe damage to the EPO or could cause damage to an identifiable individual or his or her reputation. Access control cannot be delegated by the information owner, and is restricted to registered named persons only. See here for more information. The vast majority of DG 1 documents do not fall into this category, and this is true for typical performance related data too, since even poor performance must be regarded as "normal" working behaviour and cannot be considered to actually cause damage to an individual. For strictly confidential data, additional access control measures, such as registering people with access, are already implemented where required.

04.02.21 | Author: Steve Rowan - Vice President DG1 - Patent Granting Process


In Part III, which we will publish tomorrow, lots more will be shown. ⬆

Recent Techrights' Posts

Nearly 1,000 People at EPO 'Met' to Plan Further Strikes and Impending Action to Dethrone Corrupt Leadership
Exploring the purchasing "power" of EPO leadership (buying elections while doing cocaine in public)
 
Gemini Links 24/09/2026: Laziness, Outdoor Seating, "AngelNova’s Interview Malware and Its North Korea Connection"
Links for the day
Links 24/09/2026: Slop "Linked to Disturbing Culture of Sexual Assault"; "Zelensky Warns Russia’s War Will Expand if It Is Not Ended Soon"
Links for the day
Winding-up petition served on Reform UK Party Limited (Nigel Farage)
Reprinted with permission from Daniel Pocock
Appliances Should be Dumb
Any "Smart Home Appliance" is basically a thing that does not last long, does not work as advertised, and is generally unfit for purpose
SLAPP Censorship - Part 198 Out of 200: It Sounds Like Garrett is Now Sending People to Silence Critics (Including His Own Spouse)
This week Garrett is having a somewhat karmic experience
Links 24/09/2026: Slop Contaminating KDE, Slop-Focused Data Centres Have Severe Environmental Impact
Links for the day
SLAPP Censorship - Part 197 Out of 200: Garrett Became So Poor That He Wants Others (in Another Continent) to Pay for His Own Legal Work Being Faulty
They lie to courts
The Register MS Has Become a Slopfest
This is the behaviour of a perishing publisher
Gemini Links 24/09/2026: Requiem for a Season, Philosophy, Rube-Goldberg Machine, ROOPHLOCH 2026, and Git over Gemini
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Wednesday, September 23, 2026
IRC logs for Wednesday, September 23, 2026
IBM Grapevine: Development Outsourced to LLM Slop and It Results in Many Bugs
IBM is circling down the drain and every insider knows it
Microsoft Gives Many People the 'Booty' This Week, Not Counting PIPs (Silent Layoffs and 'Voluntary' Layoffs)
Microsoft PIPs allegedly target "20-25% in some teams."
Links 23/09/2026: Pax Silica Hub Ruins a Country for a Pyramid Scheme (Slop), Convicted Felon's Press Block Resembles Iran, Russia, China
Links for the day
Gemini Links 23/09/2026: Stuck, Gambling, Fury Road, IPFS, and More
Links for the day
The Register Got Paid Today to Spew Out "AI" Almost 50 Times (Keeping the Pyramid Scheme Buzzing in Headlines)
paid-for spam
SLAPP Censorship - Part 196 Out of 200: Sending Someone to Our Doorstep to Ship Approximately 5 KG of Legal Papers (Instead of to Our Representatives)
it is not about law, this is lawfare
IBM's Anderon Already Smells Like a Fraud and IBM Insiders Heckle the Lies From the Management
Sabine Hossenfelder recently made some videos which explain in simple terms why IBM is lying and has already lied about this for years
Links 23/09/2026: Mass-Surveillance by Clownflare and "Data Centre" Crunch Commences
Links for the day
Same Name/Brand, Not the Same Project/Product
What is Linux becoming?
Germany, Like Switzerland, Will Dump Microsoft's Proprietary Software and Disservices, Then Dump Windows for GNU/Linux
This impacts not only the Windows revenue; this corrodes any "rents" Microsoft was getting from "subscriptions"
3 Years Divorced From Americans
Next year we plan to pursue the UK's Court of Appeal
The Register MS Uses Slop About Slop (in Images)
Months ago we caught The Register MS using slop for text as well
There Are Likely Over a Thousand Internet Relay Chat (IRC) Networks Online, Net Gain of 16 Seen This Month by Andreas Gelhausen's netsplit.de
It's good that they're still tracking that sort of stuff
SLAPP Censorship - Part 195 Out of 200: Two Years Since Garrett, Graveley and Lozza Worked in Parallel to Censor Techrights
It began in September 2024, shortly after we had sued Garrett
Linux Kernel Becoming a Slopfest - Part 8 - In Conclusion
this can invite more SCO-like problems in the future
Microsoft Shuts Down More Studios, Morale Low, More Mass Layoffs Ahead of Reports
They pretend it's not happening or that it's a lot smaller than it actually is
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Tuesday, September 22, 2026
IRC logs for Tuesday, September 22, 2026
Gemini Links 23/09/2026: Ljubljana, Poetry, and FORTRAN
Links for the day
The EPO's Central Staff Committee (CSC) Shows Job Insecurity at Europe's Second-Largest Institution
Who would want to join a company with such low job security?
There Are Thousands More Microsoft Layoffs (Including Silent Layoffs), Not Hundreds
Microsoft does have layoffs and today is no exception (except Microsoft talks about it)
Gemini Links 22/09/2026: Disability Studies, Slop Boosters, and TkInter
Links for the day
Links 22/09/2026: Flock is Collapsing Amid Mass Backlash and Internet Society Collaborates With the 'Epstein Class' (Trafficking of Women)
Links for the day
SLAPP Censorship - Part 194 Out of 200: The Court Needs to Also Look Into Microsoft-Controlled Restricted Boot Advanced by An American (Garrett) to Promote Monopoly and Back Doors Everywhere
Kill switch sold as 'security' is like euthanasia sold as a cure
Linux Kernel Becoming a Slopfest - Part 7 - Infested With or Plagued by Bot-Generated Slop, Committed by Microsofters
Slop is a security threat; even the person committing slop to Linux might not be aware that there's a back/bug door in the code
Raspberry Pi Has Microsoft Secrets Inside, Now DRM
now we deal with SBCs that have DRM in them, put there for commercial reasons
Edward Snowden Lost His Voice, Then His Leaks Lost Exposure (Access Denied)
When states want to deny people access to some information they have many tools at hand
2 Hours Ago The Register MS Published a Page That Says "AI" 42 Times Because It Was Paid to Do So
Still inflating the bubble for money
Gemini Links 22/09/2026: Scout Night, Cybernetic Capitalism, and Thoughts on Companies Forcing People to Adopt Plagiarism Engines
Links for the day
Links 22/09/2026: "An Arsenal of Surveillance" and Slop Bots Suggest Starting Wars
Links for the day
SLAPP Censorship - Part 193 Out of 200: Breaks GNU and Linux, Tries to Silence Critics, Loses All Money, Looks for Microsoft Allies and Sponsors
The latest emotional knee-jerk reactions serve to confirm what we have long said
Things Will Only Get Better (as We Go Backwards)
It only gets better. If you go back in time.
UK High Court Shows SRA is Totally Useless in Curbing SLAPPs, This Has Impact on Our Reporting on the SRA Next Week
We'll carry on our coverage and soon finish the current series that so we can get on with more time-sensitive ones
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Monday, September 21, 2026
IRC logs for Monday, September 21, 2026