
--Richard Stallman
LAST night we covered the use of Microsoft Skype in Sirius 'Open Source'. It only happened once, but that was enough to damage the brand and injure some workers' morale. Why would a company called "Open Source" something be eager to abandon Free/Open Source software, opting for proprietary stuff of the most vicious rival? What message does that send to longstanding clients or existing staff? What about potential/prospective/future clients and staff?
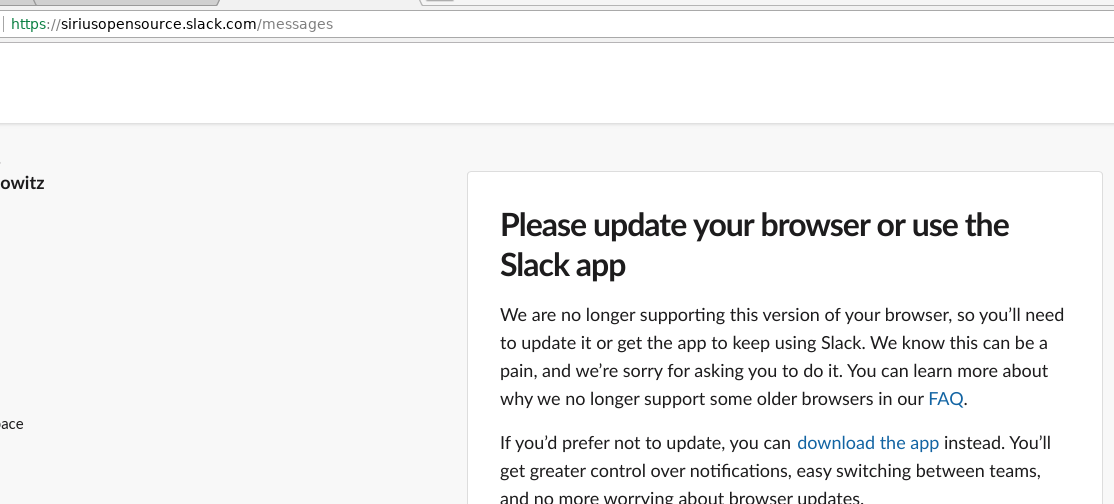
"Why would a company called "Open Source" something be eager to abandon Free/Open Source software, opting for proprietary stuff of the most vicious rival?"Slack on GNU/Linux is a mess. Slack on Free/libre browsers is almost an impossibility. So why on Earth would Sirius move away from Jabber and force/impose the use of Slack? I've uploaded 2 images from several years back; they're screenshots of what happened when I tried accessing Slack from a GNU/Linux PC using a decent Web browser that isn't controlled by spying firms:
xxxx wrote on 21/07/2019 02:23: > Hi Roy, > > You need to fix this problem and use Slack. > > You are a well qualified tech who can fix this issue and comply with > management’s request. > > As I have explicitly explained to you that you need to have your log in > for Slack and not use Rianne’s. Yet today you’re logged in via Rianne’s > and not using yours even though you sent me details of your own log in. > > To refresh your memory, this is from my previous email.
I need to install a new OS or a new browser for this.
"Slack itself has been having issues and it was sold to Salesforce."In hindsight, it seems clear this manager scared away almost all the technical people. The damage was irreversible.
Slack itself has been having issues and it was sold to Salesforce. The New York Times reported Salesforce layoffs earlier this month. The Wall Street Journal published this article noting that Slack just made bloated proprietary junk nobody truly wants to depend on:
When Salesforce Inc. bought the messaging application Slack for $27.7 billion almost two years ago, it said the marriage would “transform the way everyone works in the all-digital, work-from-anywhere world.” Corporate technology buyers so far aren’t impressed, analysts said.
The acquisition sought to capture the fast-growing market for communications and collaboration software during the Covid-19 pandemic, as employers sent workers home and shifted to remote systems.
Today, companies in the market for customer-relationship management softwareââ¬â°—ââ¬â°Salesforce’s signature productââ¬â°—ââ¬â°don’t appear to be swayed one way or another by the addition of messaging and collaboration features, said Liz Herbert, a vice president and principal analyst at information-technology research firm Forrester Research Inc.
“We don’t really see, when it comes to Slack, any pent up demand from Salesforce’s base for a tool like that,” Ms. Herbert said. “It really hasn’t become something compelling,” she said.
-------- Forwarded Message -------- Subject: ðŸâÂ¥ Slack Security Incident Date: Fri, 19 Jul 2019 16:58:59 +0000 From: Keybase <notify@keybase.io> To: r@schestowitz.com
*schestowitz*,
We've been getting questions about this, so an announcement for everyone.
Today, Slack announced that a break-in from 2015 was possibly more severe than previously announced. A lot of people have been getting emails today. It seems 1% of Slack users still had compromised accounts (after 4 years); but more seriously, Slack has not disclosed what percent of Slack teams had their messages stolen. Also, if a small fraction of users have had compromised accounts, that may still mean a majority of teams were compromised.
We're sending this note because people are now asking if this could happen with Keybase teams. Simple answer: no. While Keybase now has all the important features of Slack, it has the only protection against server break-ins: *end-to-end encryption*.
Keybase's CEO, Max, just wrote how this Slack incident personally affected him *in a new blog post* <https://keybase.io/blog/slack-incident>.
tl;dr. Hackers who break into Keybase's servers could not read your company's, family's, friend's, or community's messages. Hope this simple update answers everyone's questions.
*https://keybase.io/app*
And Keybase is free! â¤︠the Keybase team
> Hi Roy, > > You need to fix this problem and use Slack. > > You are a well qualified tech who can fix this issue and comply with > management’s request. > > As I have explicitly explained to you that you need to have your log in > for Slack and not use Rianne’s. Yet today you’re logged in via Rianne’s > and not using yours even though you sent me details of your own log in. > > To refresh your memory, this is from my previous email.
I'm going to try to install another browser, as Chome and other browsers don't work for me. They don't show anything when I log in (I sent you screenshots). Maybe I'll be logged in with my username in a few hours when it's installed (if that works).
In the meantime, I have to raise other concerns.
The inevitable has happened to Slack. They announced it days and and they can be held criminally accountable
To say that Slack got merely “compromised” would be an understatement Yes, it did in fact get compromised, but it’s a lot worse. It’s far worse than a compromise per se. I'm going to explain, starting with the basics.
Slack accumulates all data and never deletes any of it. GDPR should be applicable here and I suspect that EU authorities have not assessed that aspect just yet. What Slack is to users isn’t what it is to Slack, the company. The Electronic Frontier Foundation (EFF) issued strongly-worded warnings about Slack and even Microsoft utright banned Slack for security reasons. They very much foresaw the latest disaster. It’s difficult to assess or measure because it’s almost impossible to track the sources of rogue actors’ data.
Slack did not have a mere ‘incident’. They knew about it for quite some time (at higher levels, too). It’s the complete doomsday scenario, an equivalent of having one’s own Jabber server completely and totally hijacked, and all communications in it (names, passwords) stolen. But in the case of Slack millions of businesses are affected. In one fell swoop. Just like that. Even the public sector. Military, hospitals, you name it…
Slack got cracked, but they won’t admit that. They will lie about the extent of the damage, just like Yahoo and Equifax did (each time waiting months before revealing it was orders of magnitude worse). They game the news cycle that way. People must assume that all data is compromised. Businesses and their clients’ data is on Slack. Even HR stuff, which gets passed around in internal communications. Super-sensitive things like passwords, passports and so on.
Who was Slack data copied by? Mirrored or ‘stolen’, to put it another way? Possibly by rogue military actors that can leverage it for espionage and blackmail, as many do. Covertly. You rarely hear about blackmail because that’s just the nature of the blackmail. It happens silently. Some would say Slack got “hacked” (they typically mean cracked). But it’s actually a lot worse than getting cracked! I'll explain further…
About a month ago Slack got to its IPO milestone. But it committed an actual crime by not informing the customers of the breach. They would change passwords etc. had they known. But Slack did not obey the law. It did not inform customers. It announced all this after the IPO, in order to make shareholders liable, and it did so late on a Friday (to minimise press coverage about this likely crime). The shareholders too should sue for concealment of critical information.
Slack knew what had happened and why it waited all this time. This scandal can unfold for quite some time to come.
It would be wise to move to locally-hosted FOSS. However, that would not in any way undo the damage of having uploaded piles of corporate data to Slack and their compromised servers. In the coming days many companies will come to realise that for years they tactlessly and irresponsibly gave piles of personal/corporate data to Slack and now a bunch of crackers around the world have this data.
You can expect Slack to stonewall for a while, saying that it’s the weekend anyway. When it comes to Slack, expect what happened with Yahoo; First they say it’s a small incident; Months pass; Then they toss out a note to say it was actually big; A year later (when it’s “old news”): 3 BILLION accounts affected.
Now, like Yahoo, they will downplay scope of impact. A lot of companies can suffer for years to come (e.g. data breaches, identity theft).
I have great concern for the company where I'm working for almost a decade, including our compliance with the law and our clients' compliance with the law. This is why I bring this up.
I'm going to install something new and see if I can somehow logged in. I already tried, unsuccessfully, from two of my laptops.