
Potential Latency on Network Solutions DNS
There is a spike in DNS query volumes that is causing latency for the delay in web sites resolving. This is a result of a DDOS attack. We are taking measures to mitigate the attack and speed up queries
—————-
There may be some latency on Network Solutions DNS Severs and some queries may be timing out. This may include instances when someone types a domain name into a browser and the website will temporarily not resolve. Network Solutions Operations is working on optimizing the DNS queries and investigating the issue.
"Microsoft slammed over security advice
US COMPUTER Emergency Readiness Team (US-CERT) has warned that Microsoft's advice about how to beat the Downadup worm is flawed.
A security expert has managed to transfer the digital signature of one Windows program to another, without invalidating the signature. Didier Stevens, who presented the attack in his blog, exploited the fact that Microsoft's Authenticode code signing standard accepts the vulnerable MD5 hash algorithm. Stevens used this to generate two programs which have identical code signatures, but behave differently.
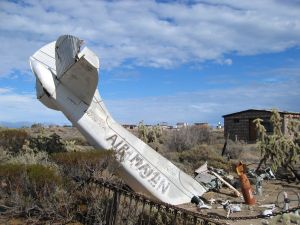
What if aircrafts accepted Microsoft quality control?
Four companies led by Dutch non-profit NLnet Labs have launched an open source, Linux-compatible DNS (Domain Name System) server. "Unbound," which is also sponsored by VeriSign, Nominet, and Kirei, claims to offer a validating, recursive, and caching DNS server that is faster than the open source DNS mainstay BIND.
Now VeriSign, the company that runs that .com and .net domains, is aiming to provide an open source alternative to BIND, called Unbound.
John Sullivan (FSF) invited me to present in this mailing list the SocialDNS project (http://www.socialdns.net). I am very interested in obtaining feedback from the GNU community because we want to submit our project to the Free Software Directory soon.
Microsoft issued a mea culpa about its DNS update on July 17, saying that the patch was crippling some machines running its Windows Small Business Server suite. Then, on July 25, it said the patch could also affect some network services on systems running Windows Server 2008, Windows Server 2003 and Windows 2000. In both instances, Microsoft detailed work-arounds.
People arrive at these pages when the domain name they request is unavailable, because, for example, they mistyped the URL. ISPs use this redirection method, known as Typosquatting, to advertise free domains or competing products. In the present case, however, clients don't arrive on the Typosquatter pages, but on pages with a crafted trojan.
The Microsoft Corp. released a DNS fix in its patch slate for July, but the company seems to have problems just getting it to end users. Moreover, some users of the DNS fix have experienced additional difficulties.
So far, since Microsoft's DNS fix was issued on July 10, there have been two separate problems associated with its installation.
From the "half truths that journo's tell" file:
I've been following the Kaminsky DNS cache exploit issue closely since it was first announced - and no doubt so has everyone else in the security business. As such I was surprised to read a headline this morning that said that Metasploit founder H D Moore (and yes Virginia, there is a Santa Claus and I run Metasploit on a test machine too - who doesn't?) had been 'owned' (should've been p'wned I think) by the DNS flaw.
The story is not true - at least according to H D Moore who claims he was misquoted by the journalist in question.
"In a recent conversation with Robert McMillan (IDG), I described a in-the-wild attack against one of AT&T's DNS cache servers, specifically one that was configured as an upstream forwarder for an internal DNS machine at BreakingPoint Systems," H D Moore wrote in a blog post. "Shortly after our conversation, Mr. McMillan published an article with a sensationalist title, that while containing most of the facts, attributed a quote to me that I simply did not say. Specifically, `"It's funny," he said. "I got owned."
As you know, 3 weeks ago I published my paper, "Microsoft Windows DNS Stub Resolver Cache Poisoning" (http://www.trusteer.com/docs/Microsoft_Windows_resolver_DNS_cache_poisoning.pdf),
simultaneously with Microsoft's release of MS08-020 (http://www.microsoft.com/technet/security/Bulletin/MS08-020.mspx). A day later, Microsoft's Secure Windows Initiative (SWI) team published their blog entry for MS08- 020 (http://blogs.technet.com/swi/archive/2008/04/09/ms08-020-how-predictable-is-the-dns-transaction-id.aspx).
Unfortunately, the SWI blog entry contains two serious mistakes. The first mistake is an inaccurate description of the PRNG used for the Microsoft Windows DNS client transaction ID. The second mistake is SWI's claim that "attackers cannot predict a guaranteed, known-next TXID exactly even with this weakness".
I contacted Microsoft about those mistakes, and while Microsoft did not refute my statements, they also refused to revise the blog entry. On one hand, I am inclined to tag this as a simple unwillingness on the side of the vendor to revise its materials and admit its mistakes. On the other hand, I cannot ignore the fact that the two mistakes, when combined, result in misleading the blog reader about the nature and the severity of the problem.
[...]
This is in stark contrast to SWI's claims. Furthermore, Microsoft did have the full paper (actually, a draft of it which contains all the relevant technical information) well before the SWI blog was published. So the problem here is not an issue of SWI not having access to the paper when they wrote their blog entry.
Microsoft is working on 133 separate updates for the problem, Budd wrote.
The concept enables malicious users to run code remotely under the system privileges generally granted to the DNS service itself.
The cmopany has been under pressure to address the flaw, reported last week, since software that exploits it has now been widely disseminated, and criminals are beginning to use it in attacks.
At least four exploits for the vulnerability in the Windows domain name system, or DNS, service were published on the Internet over the weekend, Symantec said in an alert Monday.
Cybercrooks are using a yet-to-be-patched security flaw in certain Windows versions to attack computers running the operating systems, Microsoft warned late Thursday.
How's this for a new twist on the old responsible disclosure debate: Hackers are taking advantage of information released in Microsoft's pre-patch security advisories to create exploits for zero-day vulnerabilities.
Infoblox's survey found that the number of internet-facing DNS servers increased from 9m in 2006 to 11.5m in 2007, indicative of the overall growth of the internet. Percentage usage of the most recent and secure version of open-source domain name server software - BIND 9 - increased from 61 per cent to 65 per cent over the last year. Use of BIND 8, by contrast, dropped from 14 per cent in 2006 to 5.6 per cent this year. Usage of the Microsoft DNS Server on web-facing systems also fell, decreasing to to 2.7 per cent in 2007 from five per cent last year.
The paper estimates roughly 68,000 servers on the Internet are returning malicious Domain Name System results, which means people with compromised computers are sometimes being directed to the wrong Web sites — and often have no idea.
ICANN has yet to determine the exact techniques used in the February attack. The incident will be discussed at a meeting of DNS root server operators later this month, the organization said.
Hackers launched a sustained attack last night against key root servers which form the backbone of the internet.
Security firm Sophos said that botnets of zombie PCs bombarded the internet's domain name system (DNS) servers with traffic.
"These zombie computers could have brought the web to its knees," said Graham Cluley, senior technology consultant at Sophos.
The last time the Web mob (spammers and phishers using botnets) decided to go after a security service, Blue Security was forced to fold and collateral damage extended to several businesses, including Six Apart.
To test the nation's response to a cyberattack, the Department of Homeland Security plans to hold another major exercise, called Cyberstorm II, in March 2008, Garcia said. A first such exercise happened early last year.
As if Homeland Security Secretary Michael Chertoff didn't have enough on his plate.
Not only has he had to deal with Katrina and Osama. Now he's also got to whip Steve Ballmer and the crew at Microsoft into shape. If past is prologue, that last task may be the most daunting of all.
If the United States found itself under a major cyberattack aimed at undermining the natio's critical information infrastructure, the Department of Defense is prepared, based on the authority of the president, to launch a cyber counterattack or an actual bombing of an attack source.
Comments
Needs Sunlight
2009-01-24 17:50:40
Want to run Windows? Ok, that's your right. Want to plug your Windows box to the next? Bzzzt. First time, misdemeanor + fee. Second time, misdemeanor + community service + bigger fee. Third and subsequent times, misdemeanor + hefty fine + confiscation of all electronic equipment (TV, phone, vcr, camera, computer, etc.)
DOUGman
2009-01-24 21:21:13
Education for computer use is KEY.
D.