
Bonum Certa Men Certa

Former Novell Staff Still Pushing the Linux Foundation Into Restricted Boot Territory, Ignoring the Real Threat (Back Doors)

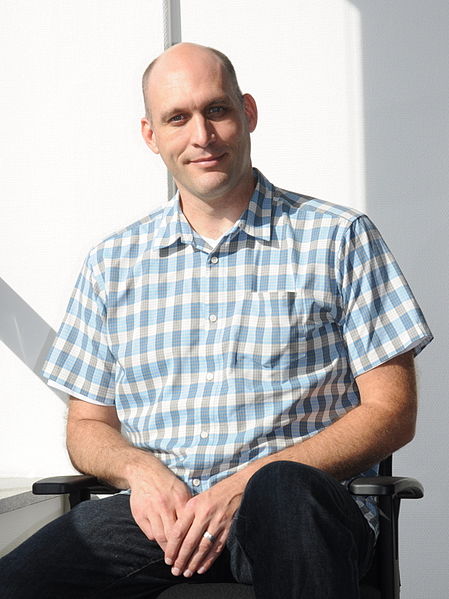
Greg Kroah-Hartman
Photo by Sebastian Oliva


Summary: Back doors in code, embedded in blobs, and even shoehorned into encryption is the overlooked security threat, which gets pushed aside in favour of phantom threats which Microsoft 'sells' through former Novell staff (i.e. funded by Microsoft)

A MONTH or two ago we mostly ignored exaggerated (sexed-up) reports about something called "Hand of Thief". When there's a Windows security threat the press does not call out Windows, but when it relates to GNU/Linux then tabloids like ZDNet scream from the rooftops. This thing called "Hand of Thief" is basically a malicious program which GNU/Linux users need to install themselves in order for it to do malicious things. It is not a virus, it does not spread, and it hardly even uses social engineering to get itself installed. We cited some reports which stress these facts and now comes a belated one too [1]. LynuxWorks is now offering some "Linux rootkit detector" [2] as if rootkits on GNU/Linux are a common issue. In a sense, since the Linux Foundation seems to insist on helping UEFI restricted boot, we are led to the belief that bootkits are a common threat to Linux. As the Linux Foundation's site put it, as in the words of the employee it acquired from Novell:


Now that The Linux Foundation is a member of the UEFI.org group, I’ve been working on the procedures for how to boot a self-signed Linux kernel on a platform so that you do not have to rely on any external signing authority.


Greg K-H has been working on all sorts of other kernel-level projects that help Microsoft. He did this while being paid by Novell, which was in turn being given money by Microsoft. That's the power of money. Other former Novell employees also helped promote UEFI restricted boot, as we showed before. Rogue influence by Novell in the Linux Foundation is a subject we have written about for half a decade, showing numerous examples.

The bigger security issue right now might be back doors, which might also exist in Linux, even in encryption form [3] (giving away passwords over the network for example), so hard-to-crack passwords [4] might not be enough. Microsoft's and Sony's network compromises sure reveal the massive financial effects of system intrusions, so this subject should not be taken lightly.

UEFI restricted boot is actually a security threat, not a security solution, especially when a signature is provided and managed by some rogue company in the United States -- one which has been secretly in bed with the NSA. With UEFI restricted boot, hardware can be bricked remotely. In a way, UEFI restricted boot deserves the name "unsecure boot". In some devices it can block the user from accessing his/her own computer. Nobody should promote such treacherous computing.

Related/contextual items from the news:


  1. Hand of Thief, Not
    Linux's biggest vulnerability is the software that users install with full "superuser" privileges. If you just install applications from your distro's official repository, that's not a problem. But if you download software from dubious web sites, or if you add a mysterious repository to your package manager, you're opening yourself up for an infection. Always, always make sure you know what software you are installing, why you are installing it, and where it's from.


  2. Linux rootkit detector adds hardware punch to security scanning
    LynuxWorks is stepping up the battle with the release of the first hardware-based rootkit detection system powered by the LynxSecure separation kernel. Called the RDS5201, it combats and detects stealthy advanced persistent threats. Built on the LynxSecure 5.2 separation kernel and hypervisor, this small form factor appliance has been designed to offer a unique detection capability that complements traditional security mechanisms as they try to protect against the growing number and complexity of cyber threats.


  3. RSA warns developers not to use RSA products
    In today's news of the weird, RSA (a division of EMC) has recommended that developers desist from using the (allegedly) 'backdoored' Dual_EC_DRBG random number generator -- which happens to be the default in RSA's BSafe cryptographic toolkit. Youch.
  4. How-to make hard-to-crack passwords you can easily remember


  5. Australian who boasted of hacking to plead not guilty to charges stemming from raid
    Dylan Wheeler, who claimed in February to have breached Microsoft's and Sony's networks, has not been charged with hacking


Recent Techrights' Posts

Enjoy the Giving/Sharing, Not Taking
We've long supported what we believed in, even with the little money we had
SLAPP Censorship - Part 190 Out of 200: Plagiarism, Back Doors, and Sabotage of Linux
This can go on for a decade or longer
 
Links 20/09/2026: "Google Now Asking For Users’ Video Selfies" and Energy Prices Set to Rise
Links for the day
Links 20/09/2026: Amazon Layoffs, Flock 'Buyouts' (Silent Layoffs)
Links for the day
USCIS and Microsoft Rumours: Curbs on Lowering Salaries by Importing Cheaper Replacements?
It seems like Microsoft's mass layoffs and efforts to cheapen the workforce face obstacles
Gemini Links 20/09/2026: "Music While Working" and Radio Silence
Links for the day
Clownflare Data From Canada
We've like to think many people are attempting to install GNU/Linux over the weekend
Linux Kernel Becoming a Slopfest - Part 5 - Kernel Dependency on Plagiarism Giant Microsoft is a Death Blow to Any Kernel
Microsoft is bringing copyright-infringing slop into Linux
GNU/Linux Has Grown a Lot Lately
Based on Clownflare
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Saturday, September 19, 2026
IRC logs for Saturday, September 19, 2026
Links 19/09/2026: Many Patents Become Candidates for Annulment and Linux [sic] Foundation Takes More Slop Money to Promote Malicious Bots
Links for the day
Gemini Links 19/09/2026: The Fundamental Human Assets, The History of Gopher's "i" Type, and ROOPHLOCH 2026
Links for the day
Links 19/09/2026: "OpenAI and Microsoft Knew They Were Starting a ‘Doom Loop’ [of Mass Plagiarism 'Normalised' by Brute Force] for the web", Calling It "Hey Hi"
Links for the day
8 Series Going on at the Moment in Techrights
4 series about SLAPPs and related matters
Linux Kernel Becoming a Slopfest - Part 4 - Outsourcing to Microsoft, Approaching 10 Gigabytes
Can we blame Microsoft for those DDoS attacks? Partly.
SLAPP Censorship - Part 189 Out of 200: A Terrible Idea to Condemn Projects for Using Slop 'Code' When Your Own Employer Does This (and Profits From Every Company Doing So) or to Call Distros 'Not Secure' While You Advance Back Doors
"I don’t want a back door. I want a front door."
Software Freedom Day 2026 is Today, Week-long Celebration in Brazil
In Brazil, Clownflare reckons about 1 in 20 laptops/desktops might use GNU/Linux already
Red Hat Lost 2,000 Staff (Net Loss)
Maybe by year's end it'll be a 20% reduction
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Friday, September 18, 2026
IRC logs for Friday, September 18, 2026
Gemini Links 18/09/2026: Setting Goals, Tiredness, and Admissions From LLM Purveyors It Was All Along About Building Plagiarism Engines Sold as "Intelligence"
Links for the day
Links 18/09/2026: Microsoft Boasted Slop is Just Copyright Infringement/Plagiarism, Floods in Europe
Links for the day
Slop Ruins Development and Reverse Engineering, It Rewards Retarded "Slop Kiddies" (to Quote Andy ‘TheFlow0’ Nguyen)
Slop is just a fatal cancer that kills the body, then dies with the body it killed
Internet Relay Chat (IRC) and Mailing Lists Are Still Better Than Discord, Slack, and Discourse
Discourse is "open" "bossware"
Links 18/09/2026: Disgust Over LLMs and Why "Agents" (Bots) Are Nothing More Than "Spam"
Links for the day
Software Freedom Day is Tomorrow
events coming
Illegal and Unconstitutional Tribunal That SLAPPs Critics Does the Illegal and Unconstitutional: It "Rubberstamps Software Patents"
This is not a legal system. This is mafia.
Privilege in 'Linux' Foundation (Double Standards) and What the FSF Should Avoid Doing
If RMS can talk about politics, others too should be able to talk about politics
Seems Like Many Microsoft Layoffs Are Going On Right Now (Forever Layoffs)
Like IBM, Microsoft hopes shareholders will not know of morale and financial problems
More Threats From the Person of Restricted Boot Infamy
Remember this is the man who is the principal purveyor of restricted boot and who landed restricted boot in Linux
Snooping EPO Management, Sniffing Up Every Staff Action
It this a problem for whistleblowers? Of course.
Don't Do That
Options do exist. People should exercise freedom.
Iran Has Debunked GAFAM and Cloud Computing as Safety of Data
Cloud of smoke?
Over at Tux Machines...
GNU/Linux news for the past day
IRC Proceedings: Thursday, September 17, 2026
IRC logs for Thursday, September 17, 2026
SLAPP Censorship - Part 188 Out of 200: Used, Then Discarded, by Microsoft (as We Predicted All Along, It's Always Like That)
The longer they carry on with it, the more scandalous this will get
Linux Kernel Becoming a Slopfest - Part 3 - Besieged by LLM Bots, Now Hiding Behind a Wall of JavaScript
The series began 3 days ago
Gemini Links 18/09/2026: Modern Linguistic, Boxing, Turning 40, and Solar MiniServer
Links for the day